Pico HSM Cipher
Use HSM > Management > Cipher in PicoKey App to run operations with an existing key.
The Cipher tab runs cryptographic operations using the selected Key ID.
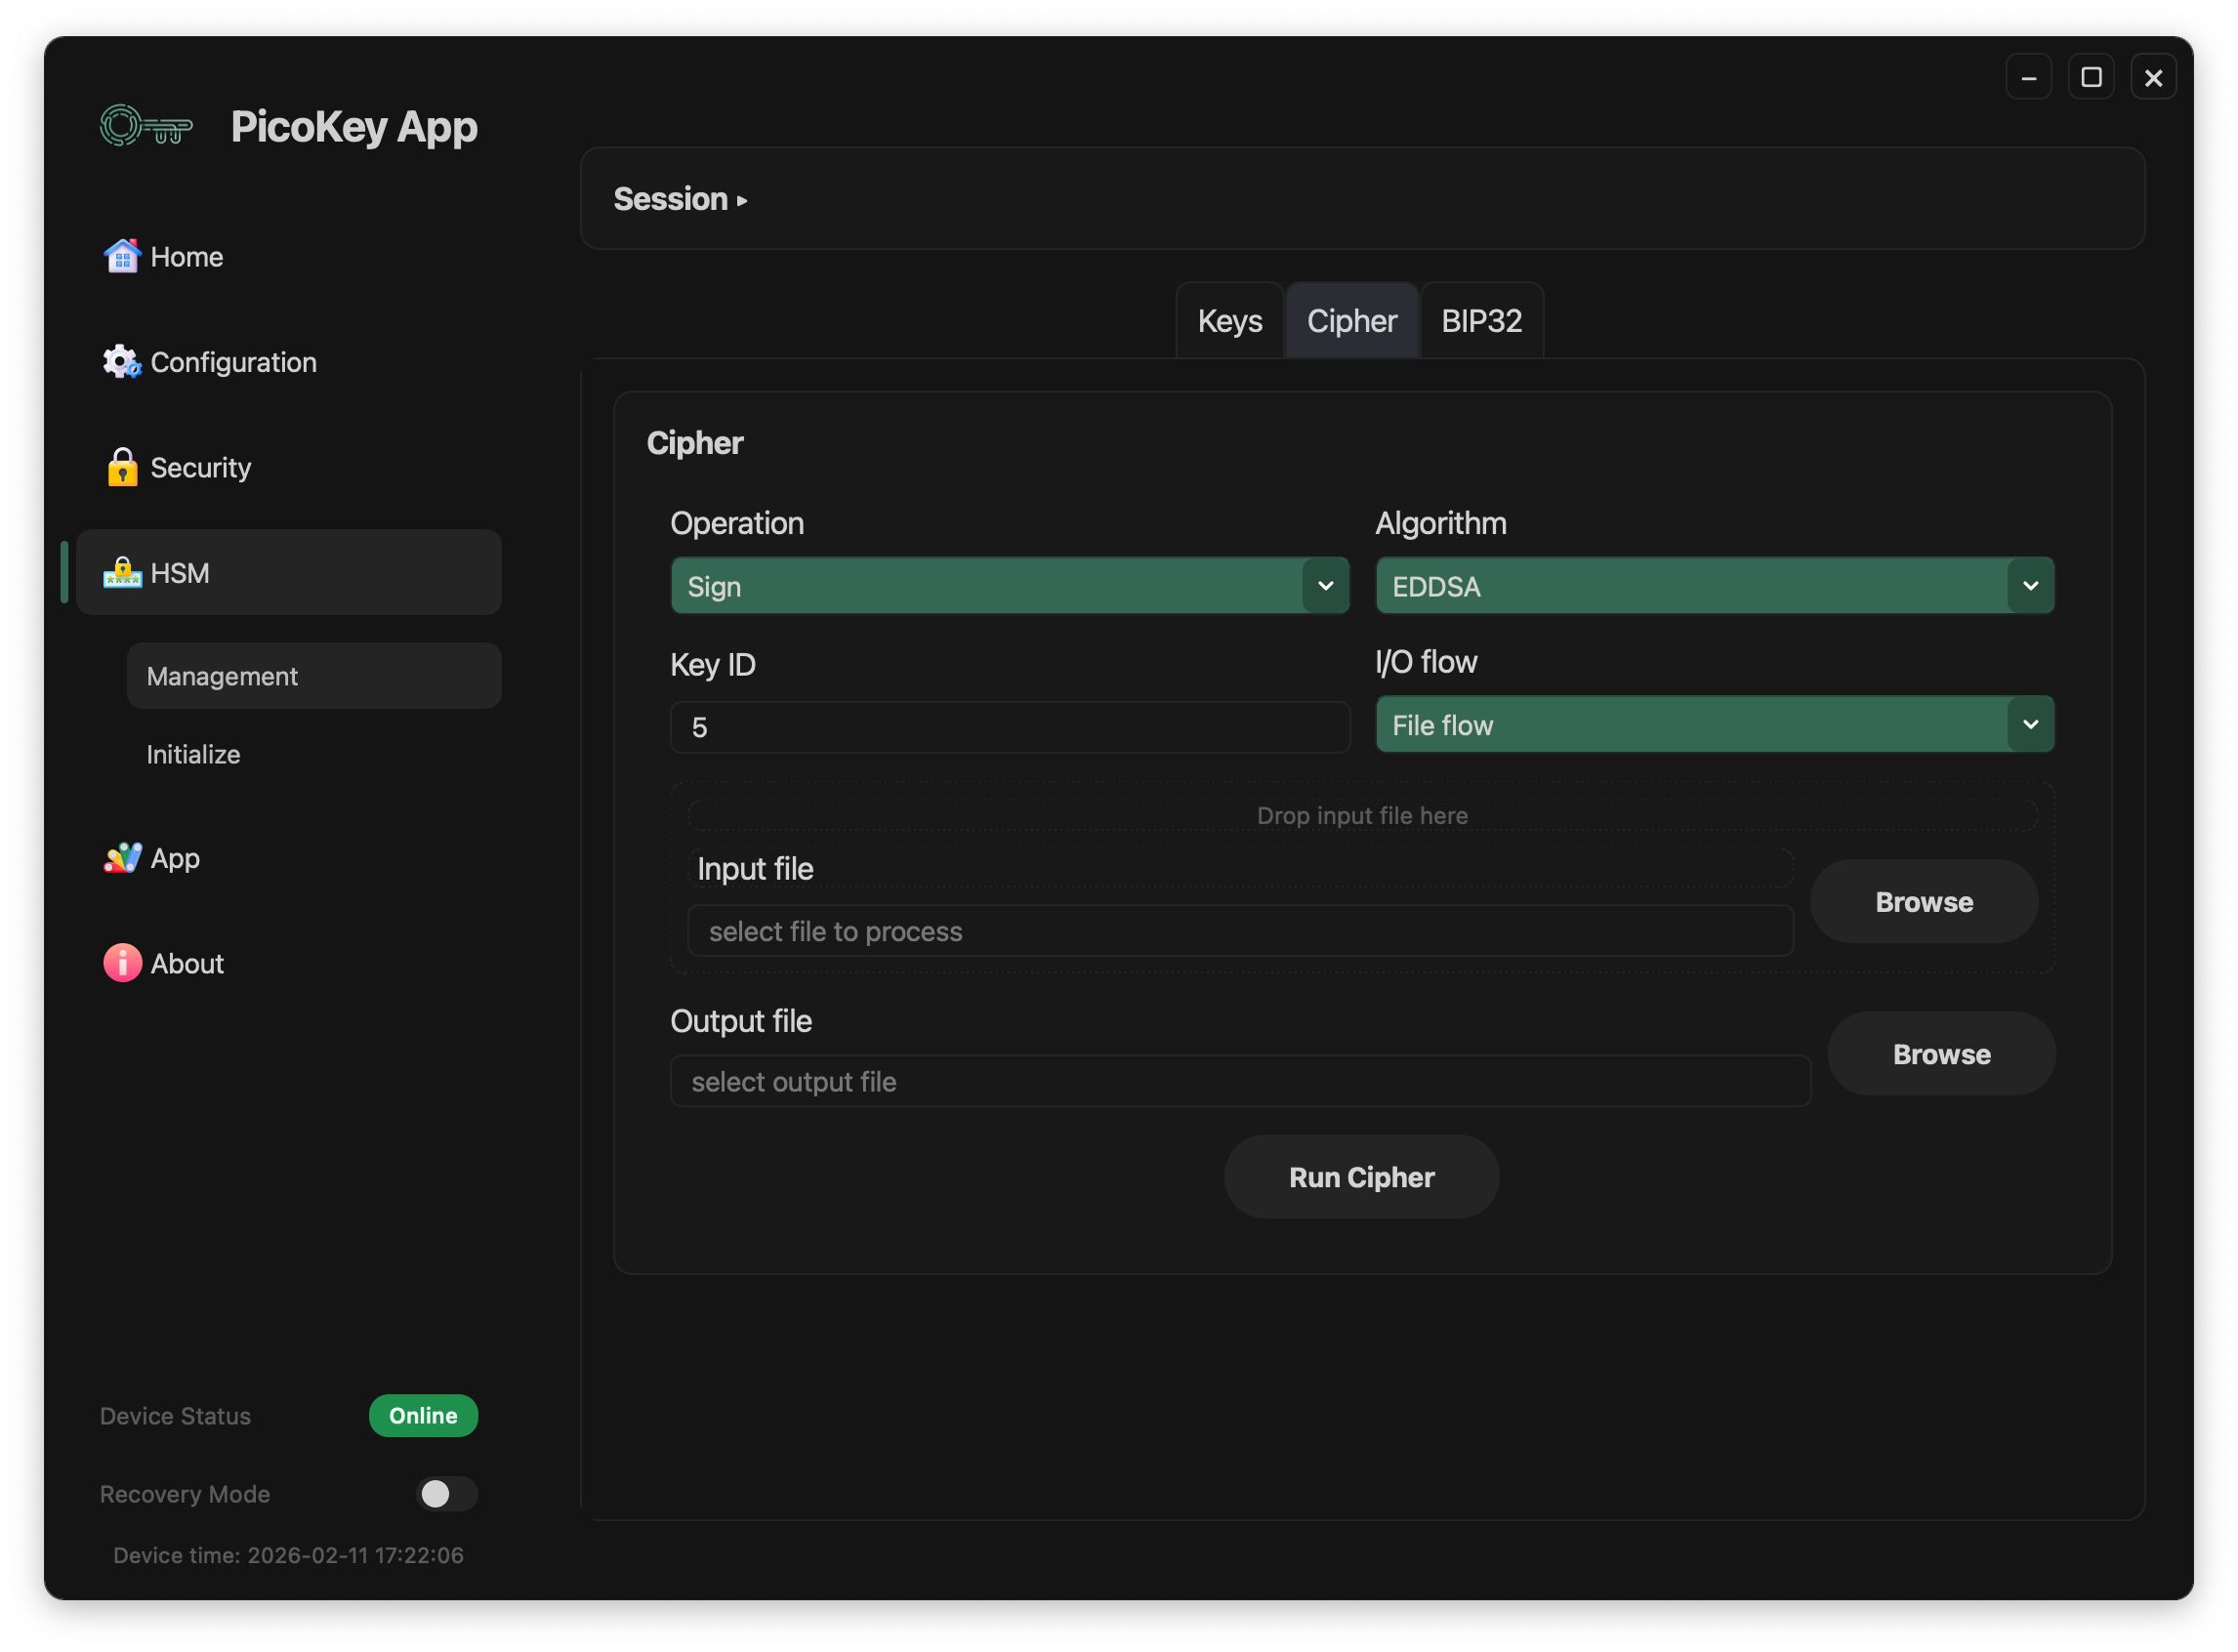
Prerequisite
Before you run an operation:
- Go to
HSM > Management. - Enter
PIN. - Click Unlock.
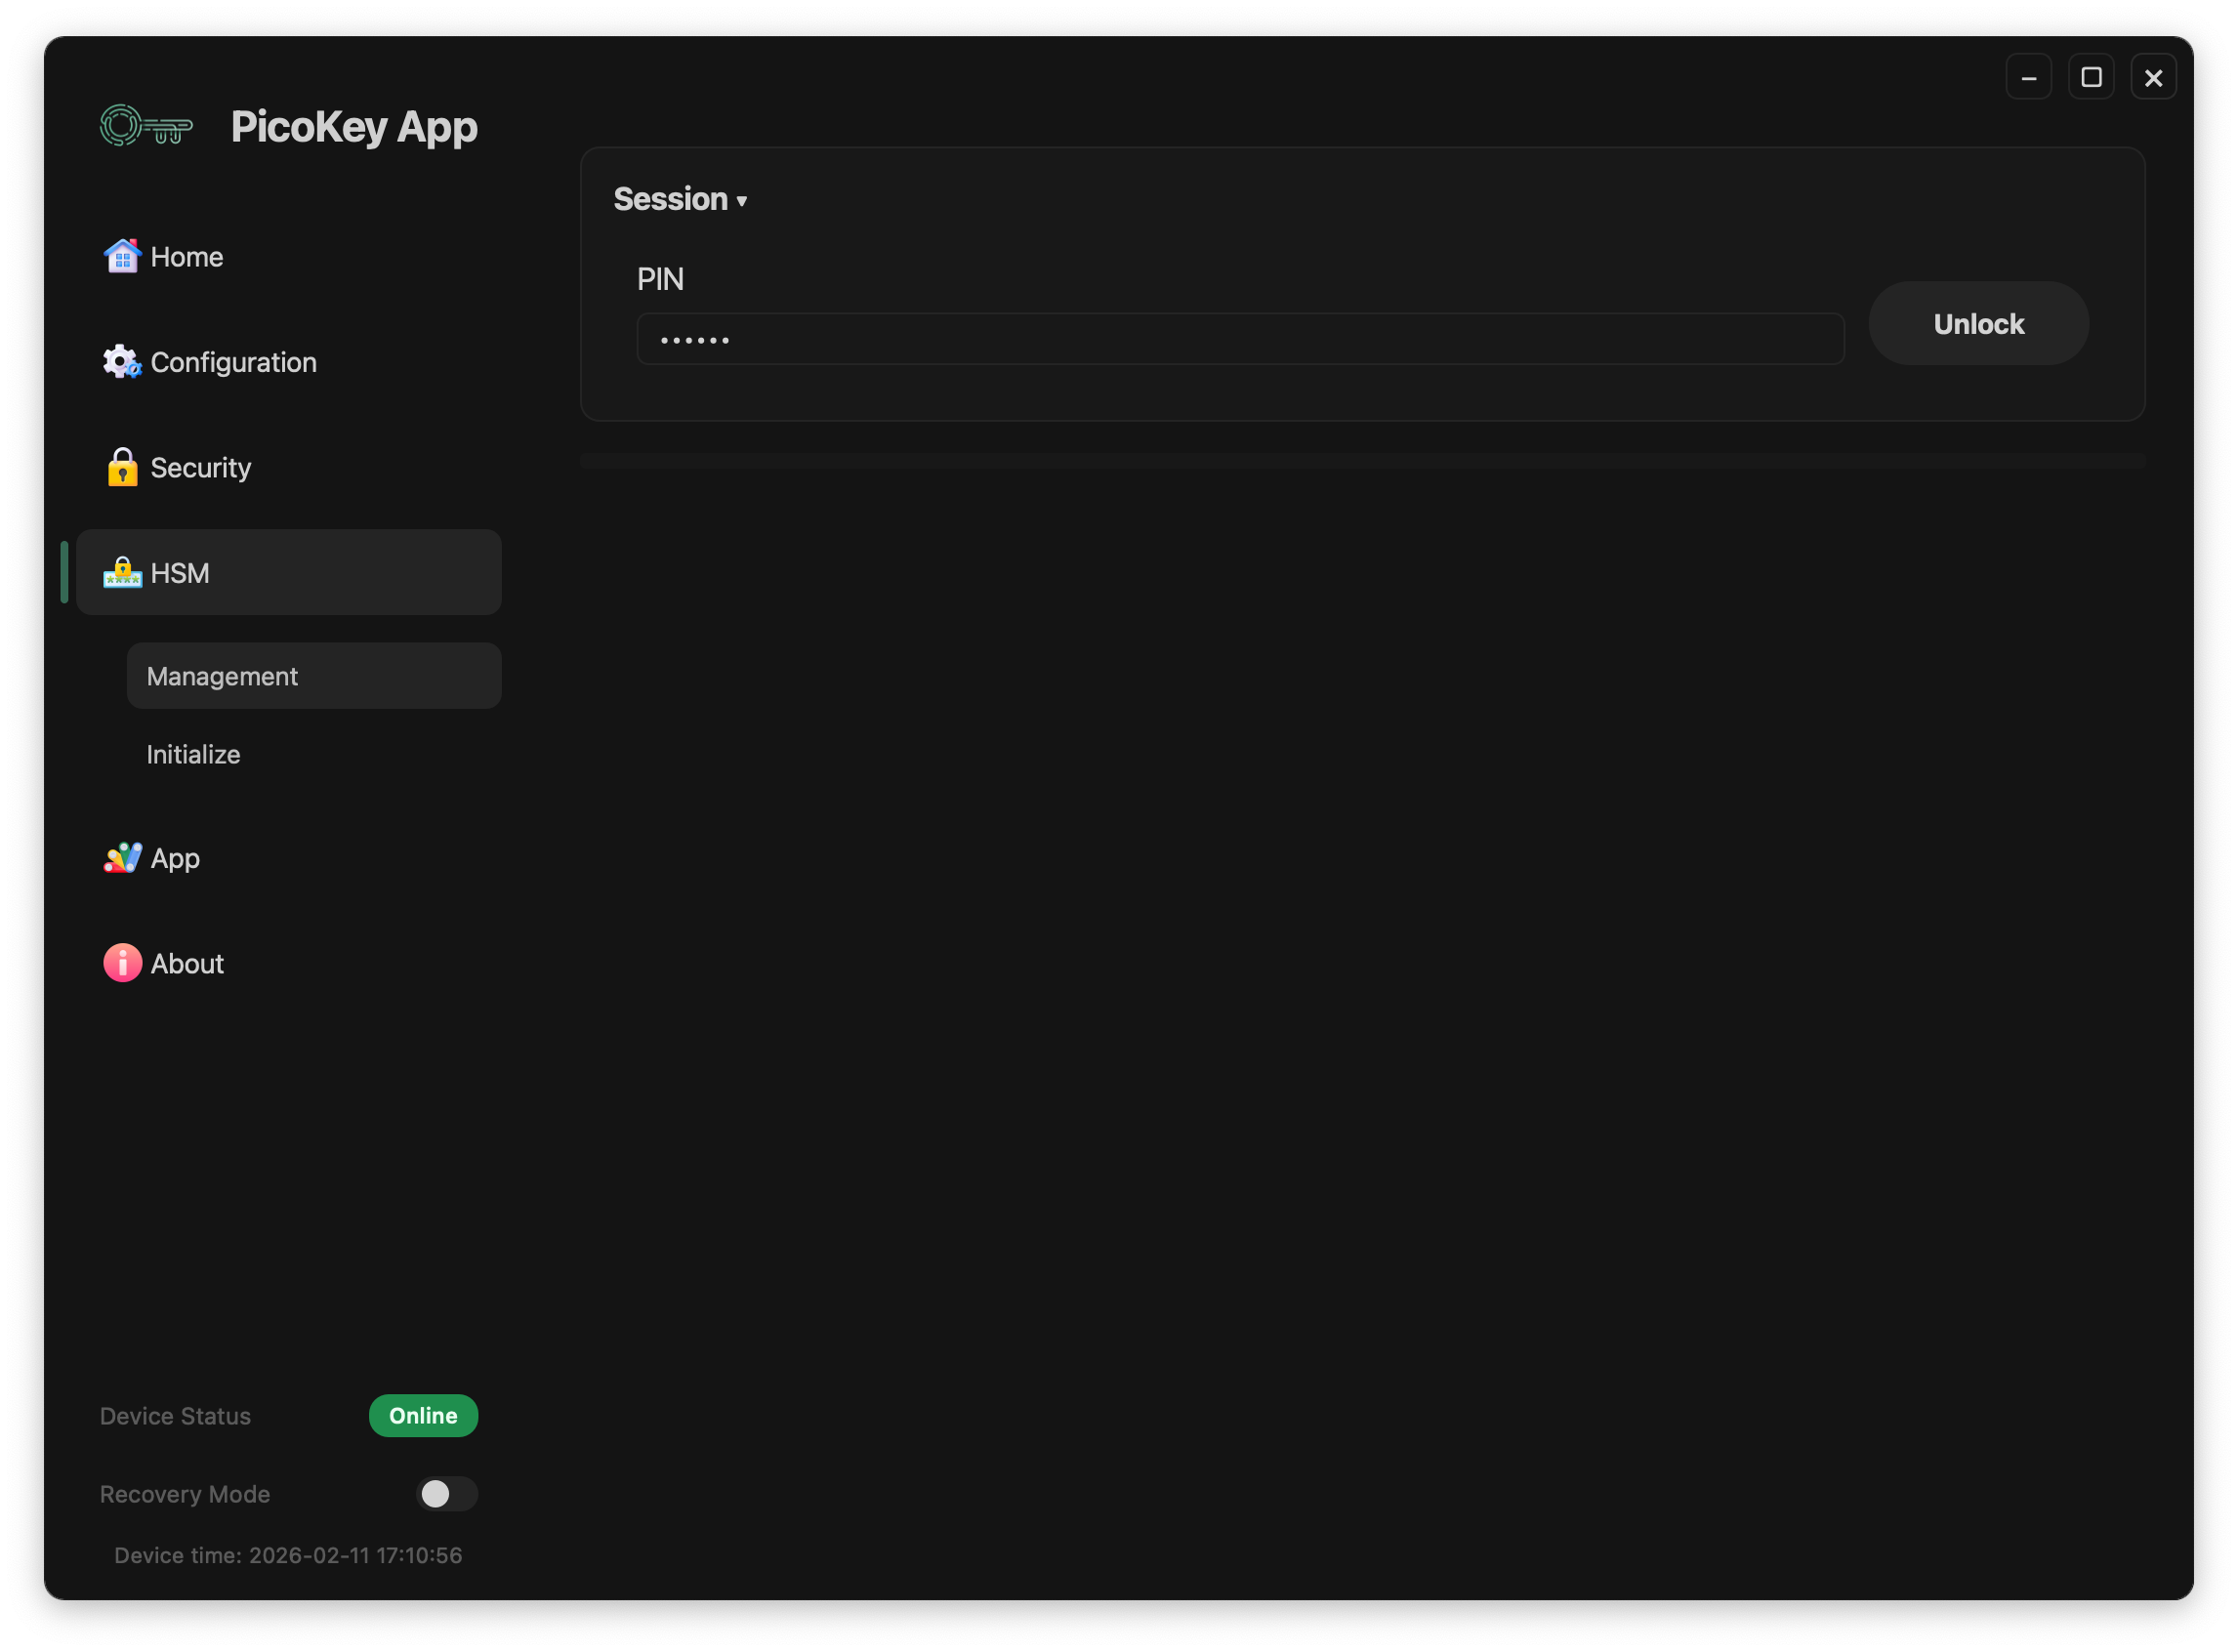
- Wait until keys are loaded.
- If needed, expand
Sessionand use Reload / Change PIN. - Use a valid
Key ID.
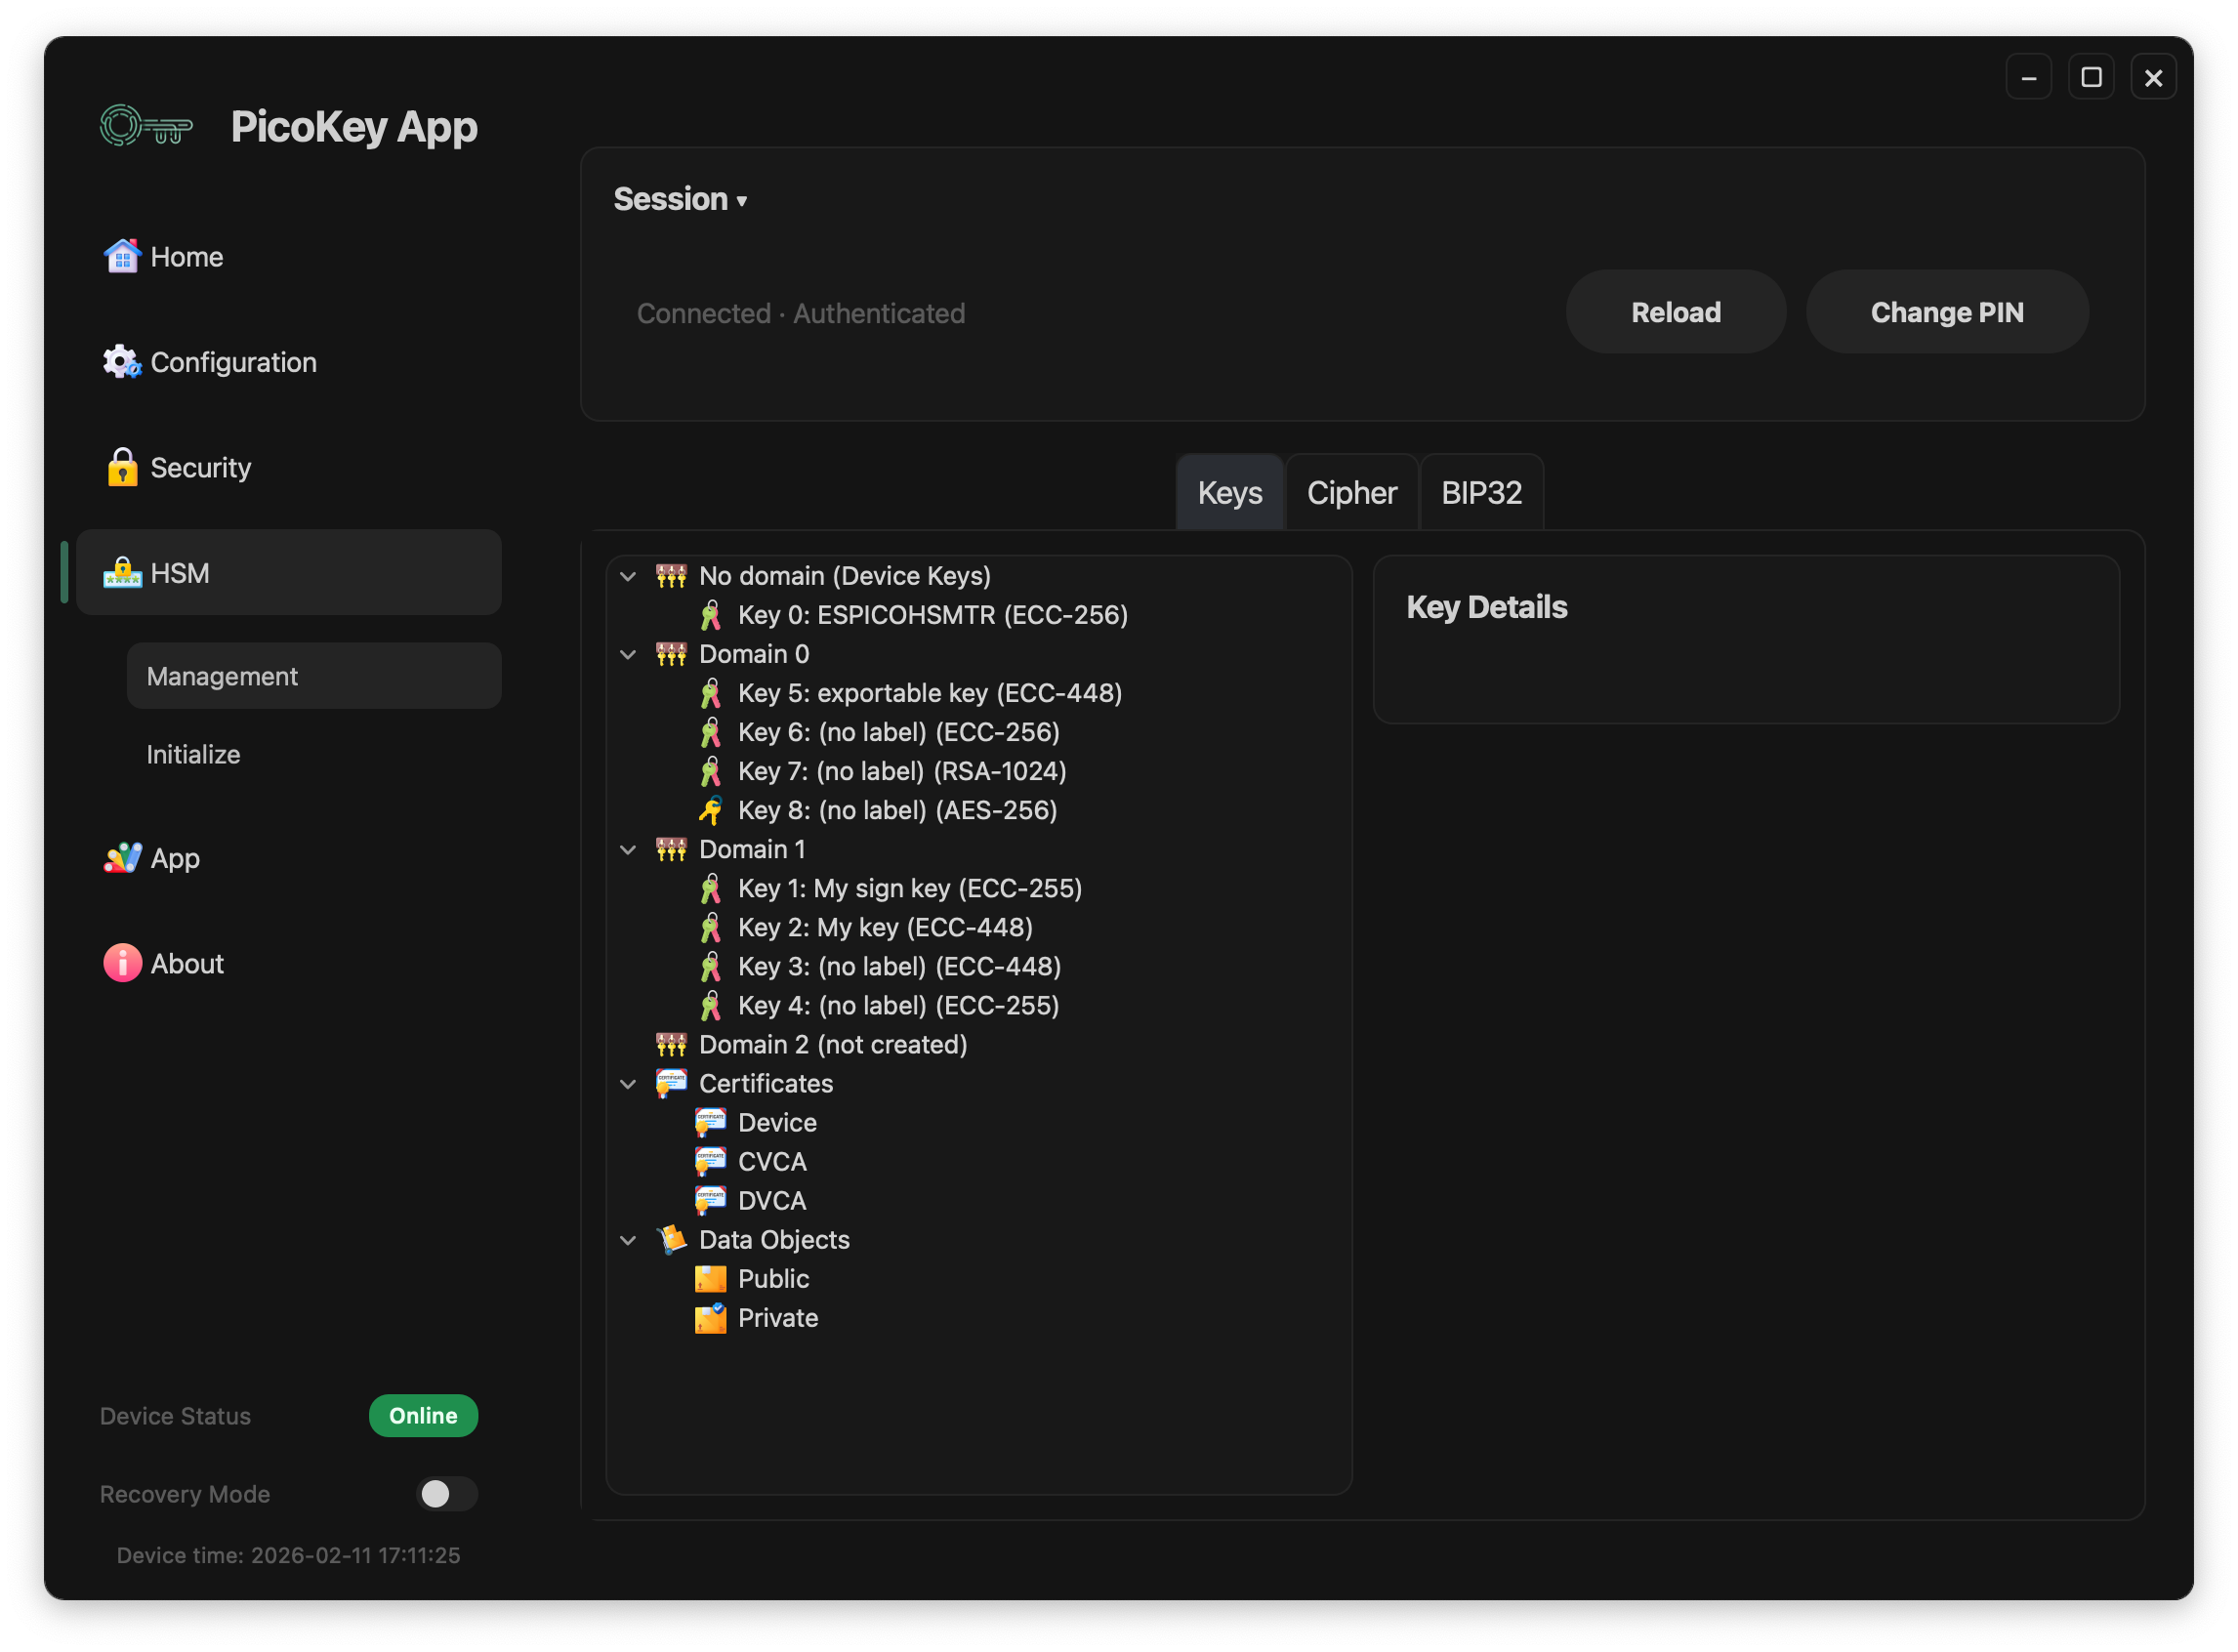
Main controls
- Operation:
Sign,Decrypt,Encrypt,MAC,KDF - Algorithm: available values depend on key type and selected operation
- Key ID: key handle used by the operation
- I/O flow:
File floworText box flow - Run Cipher: executes the selected operation
I/O flow
Choose between two input and output modes.
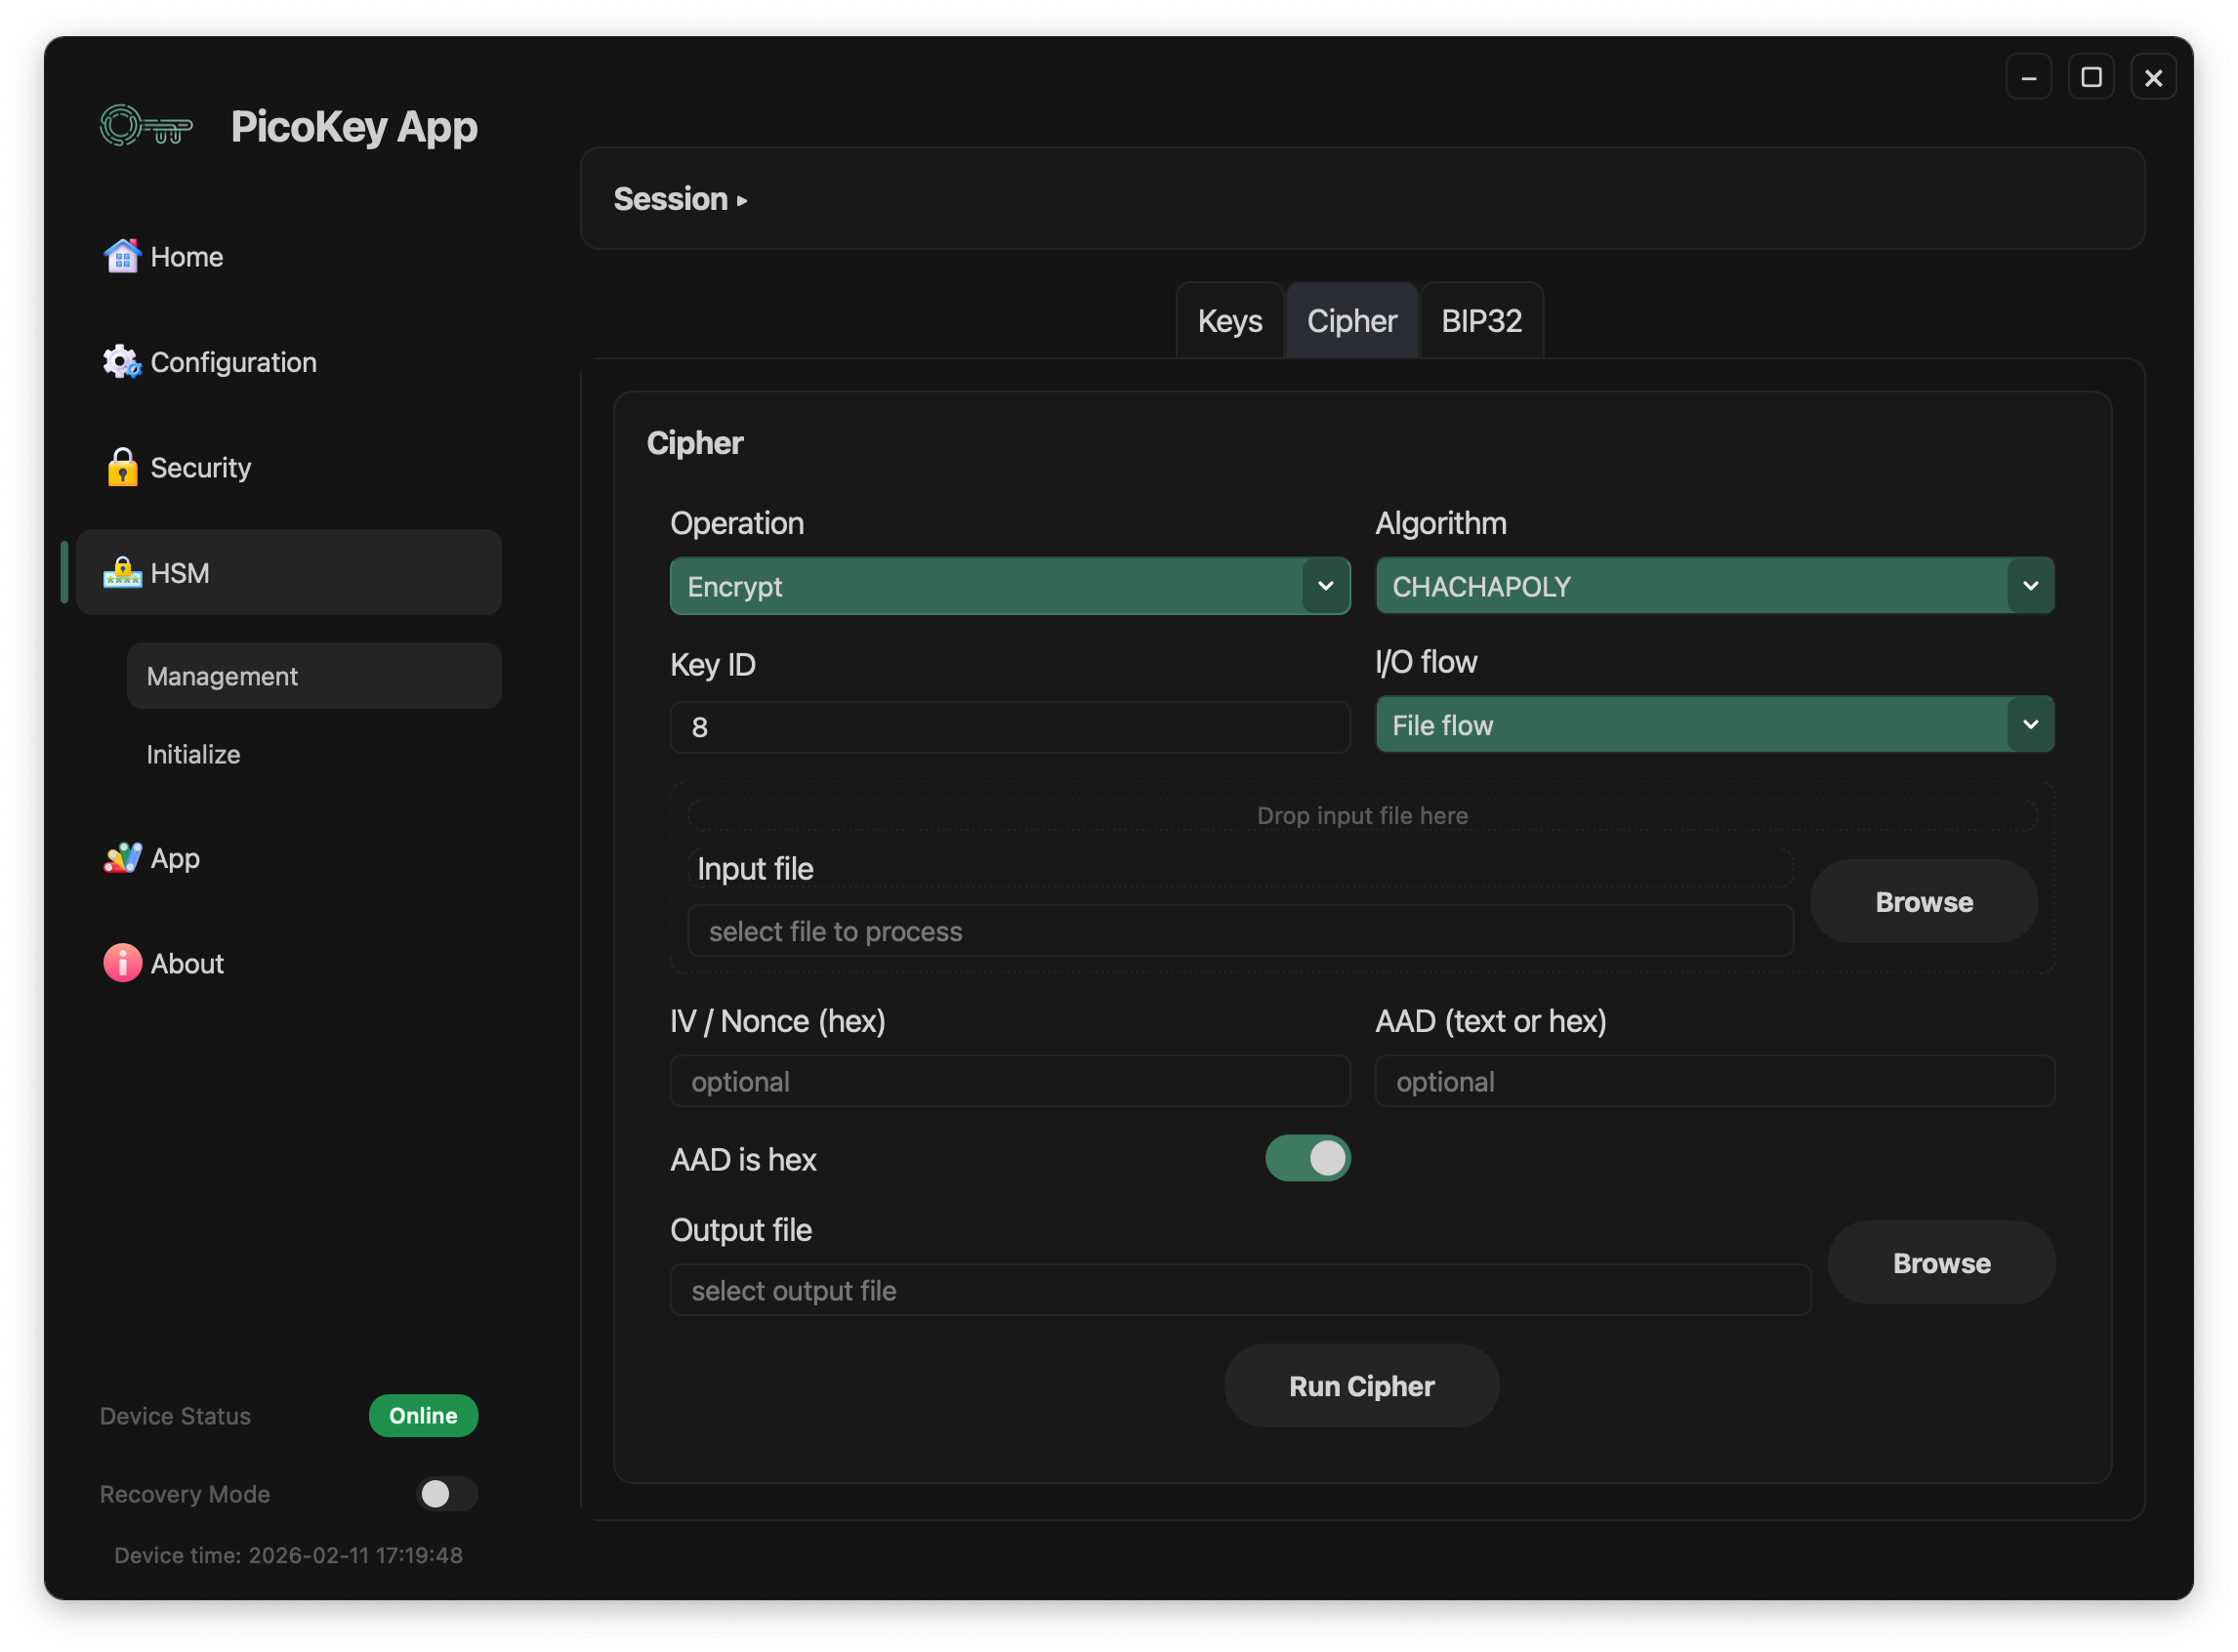
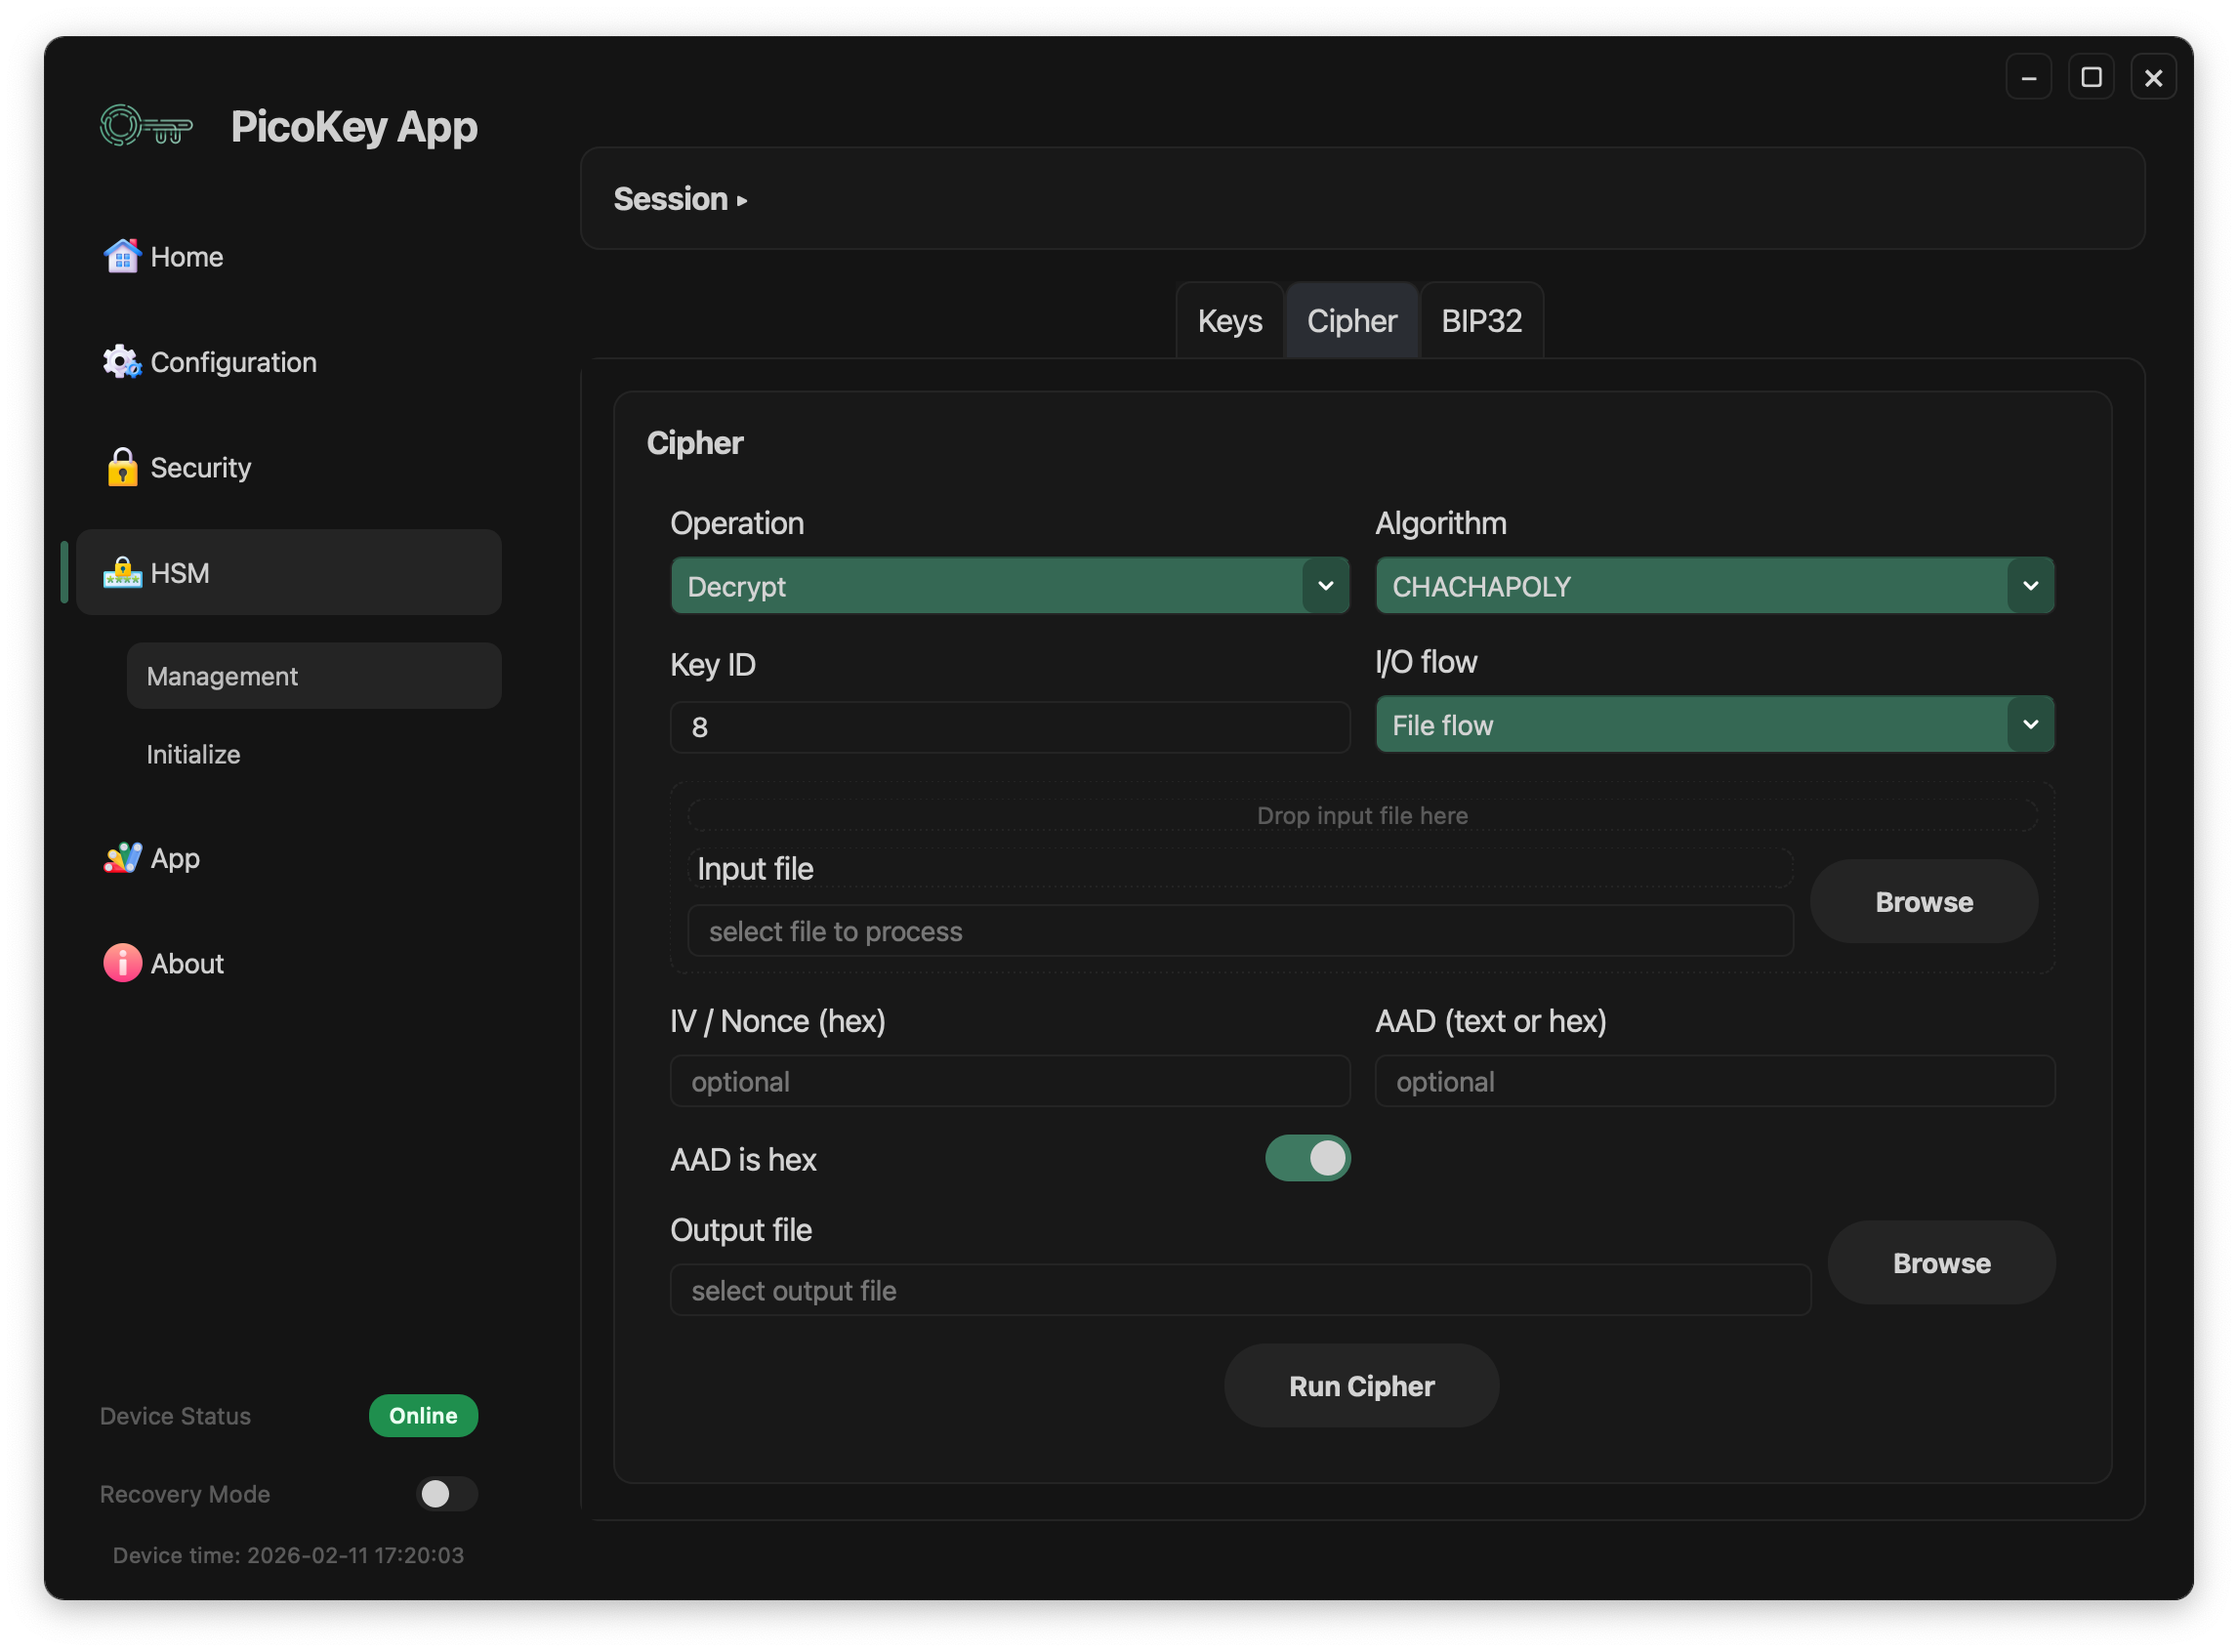
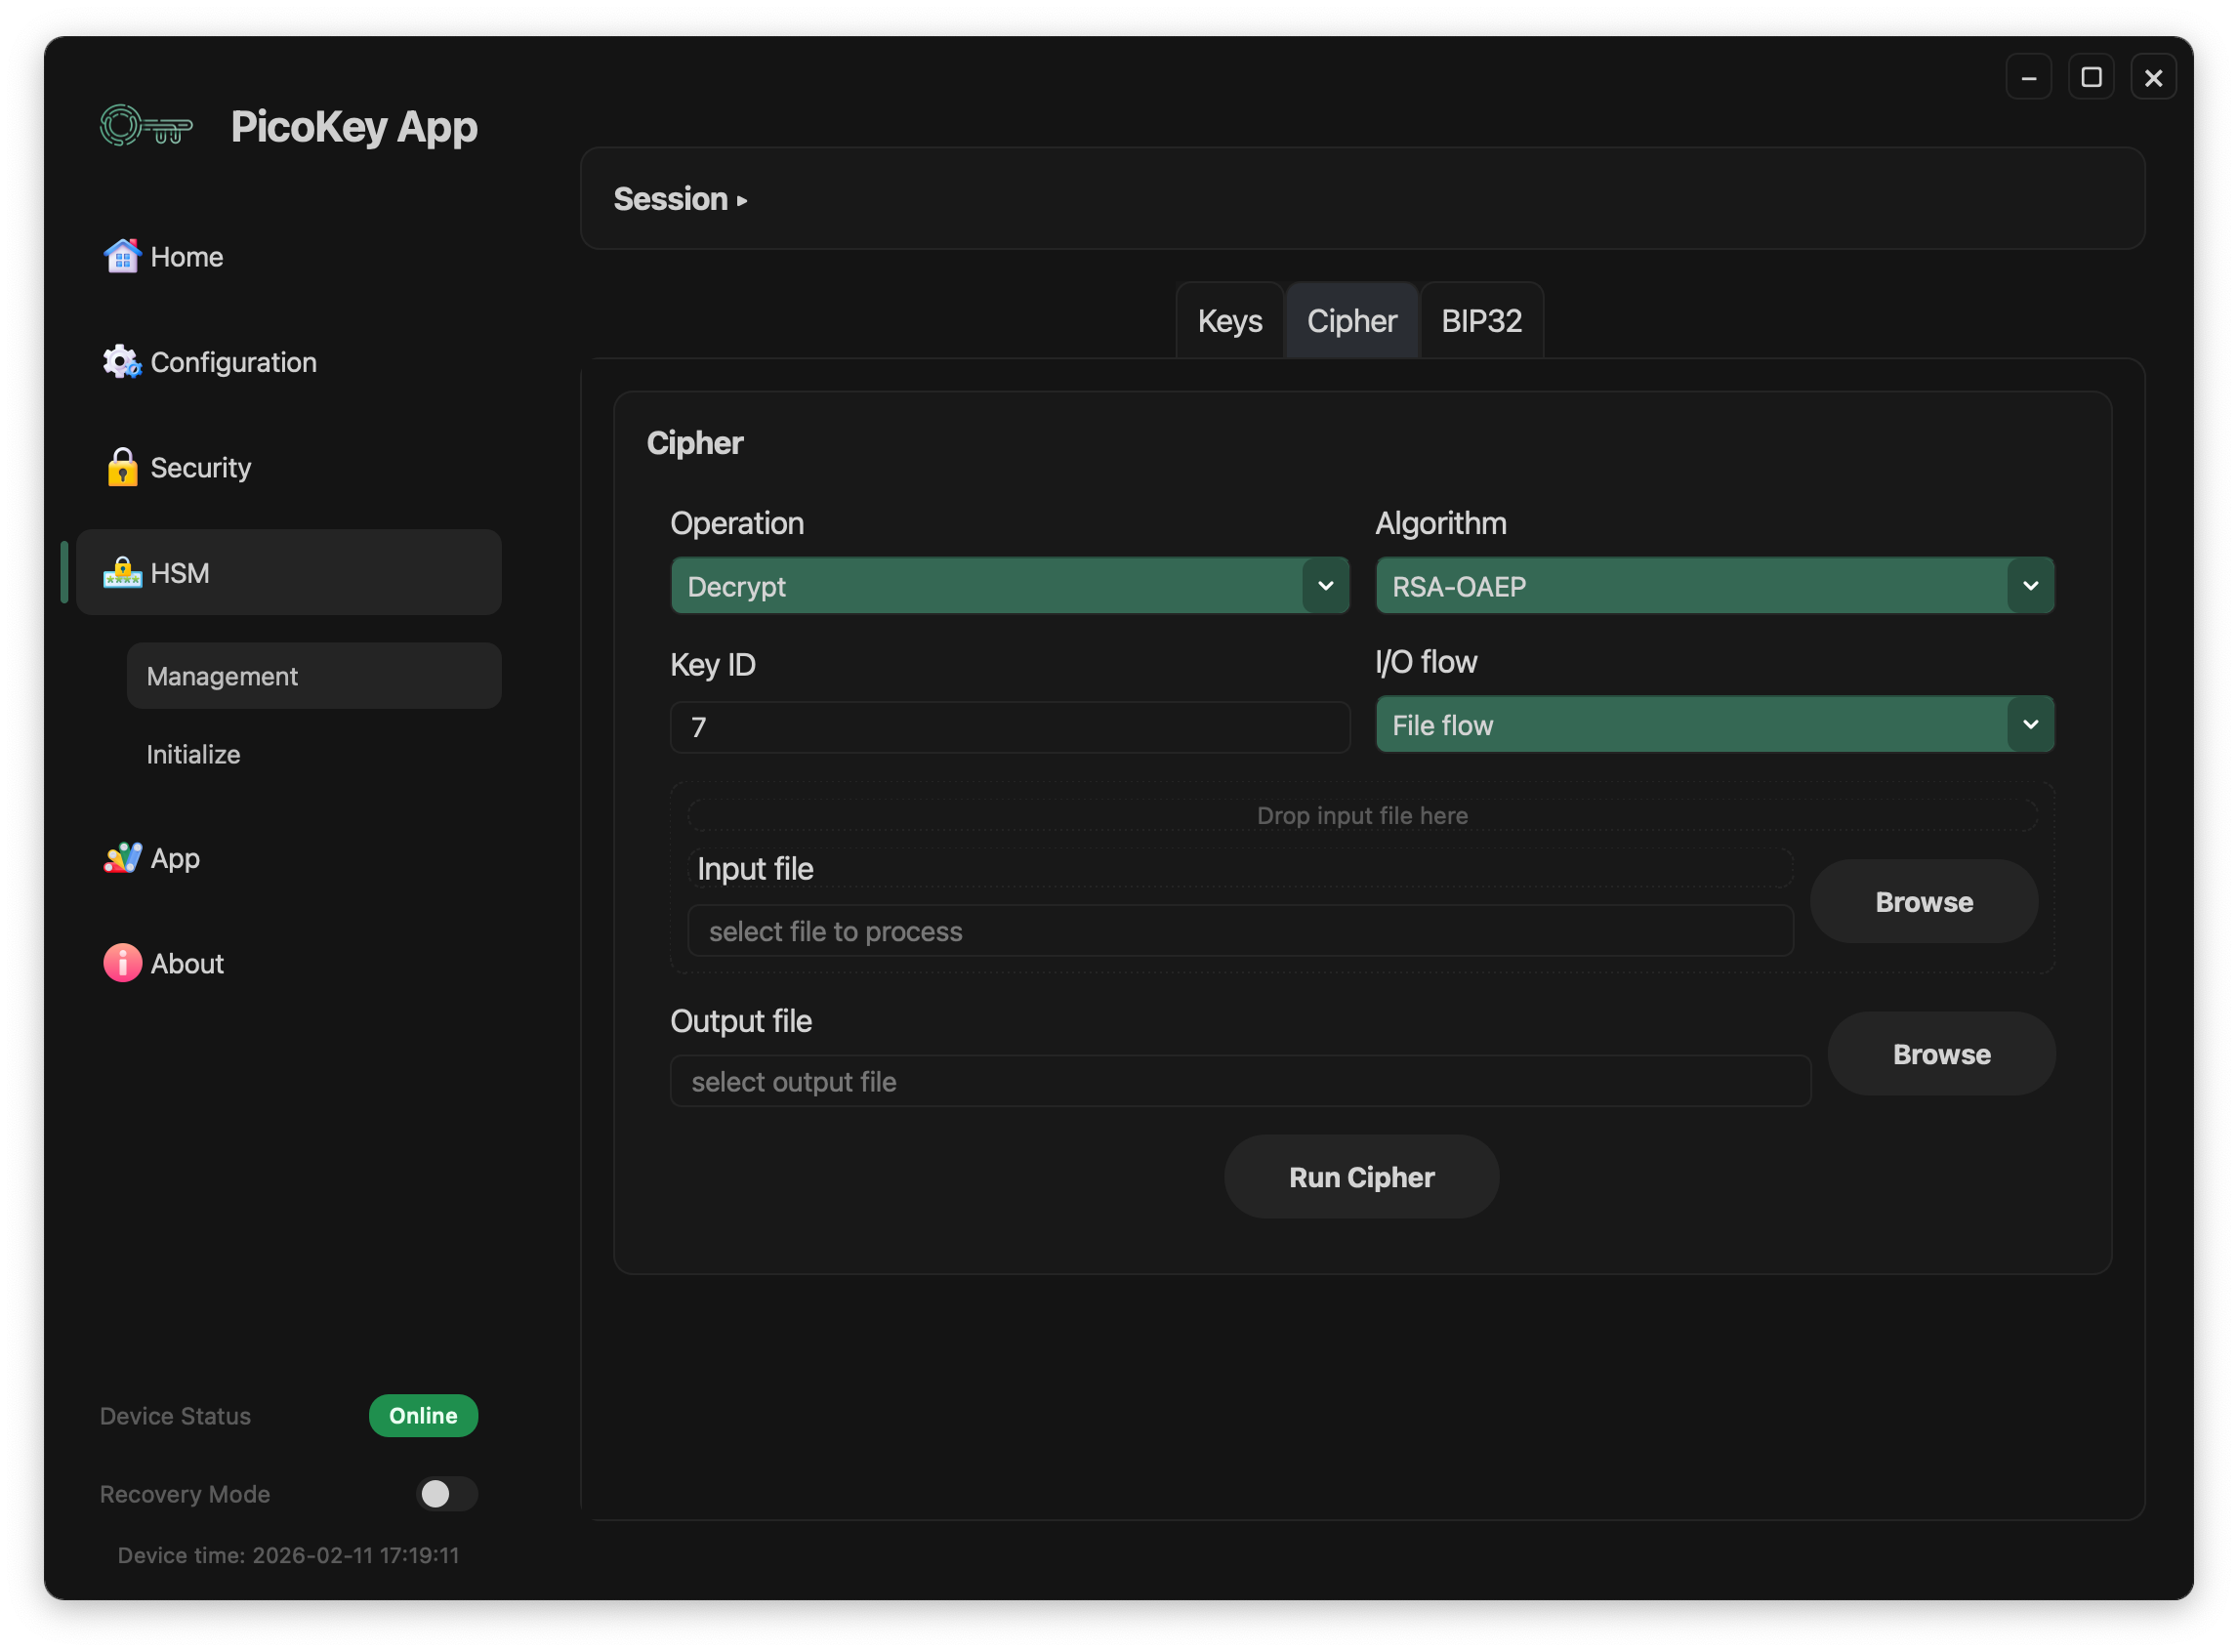
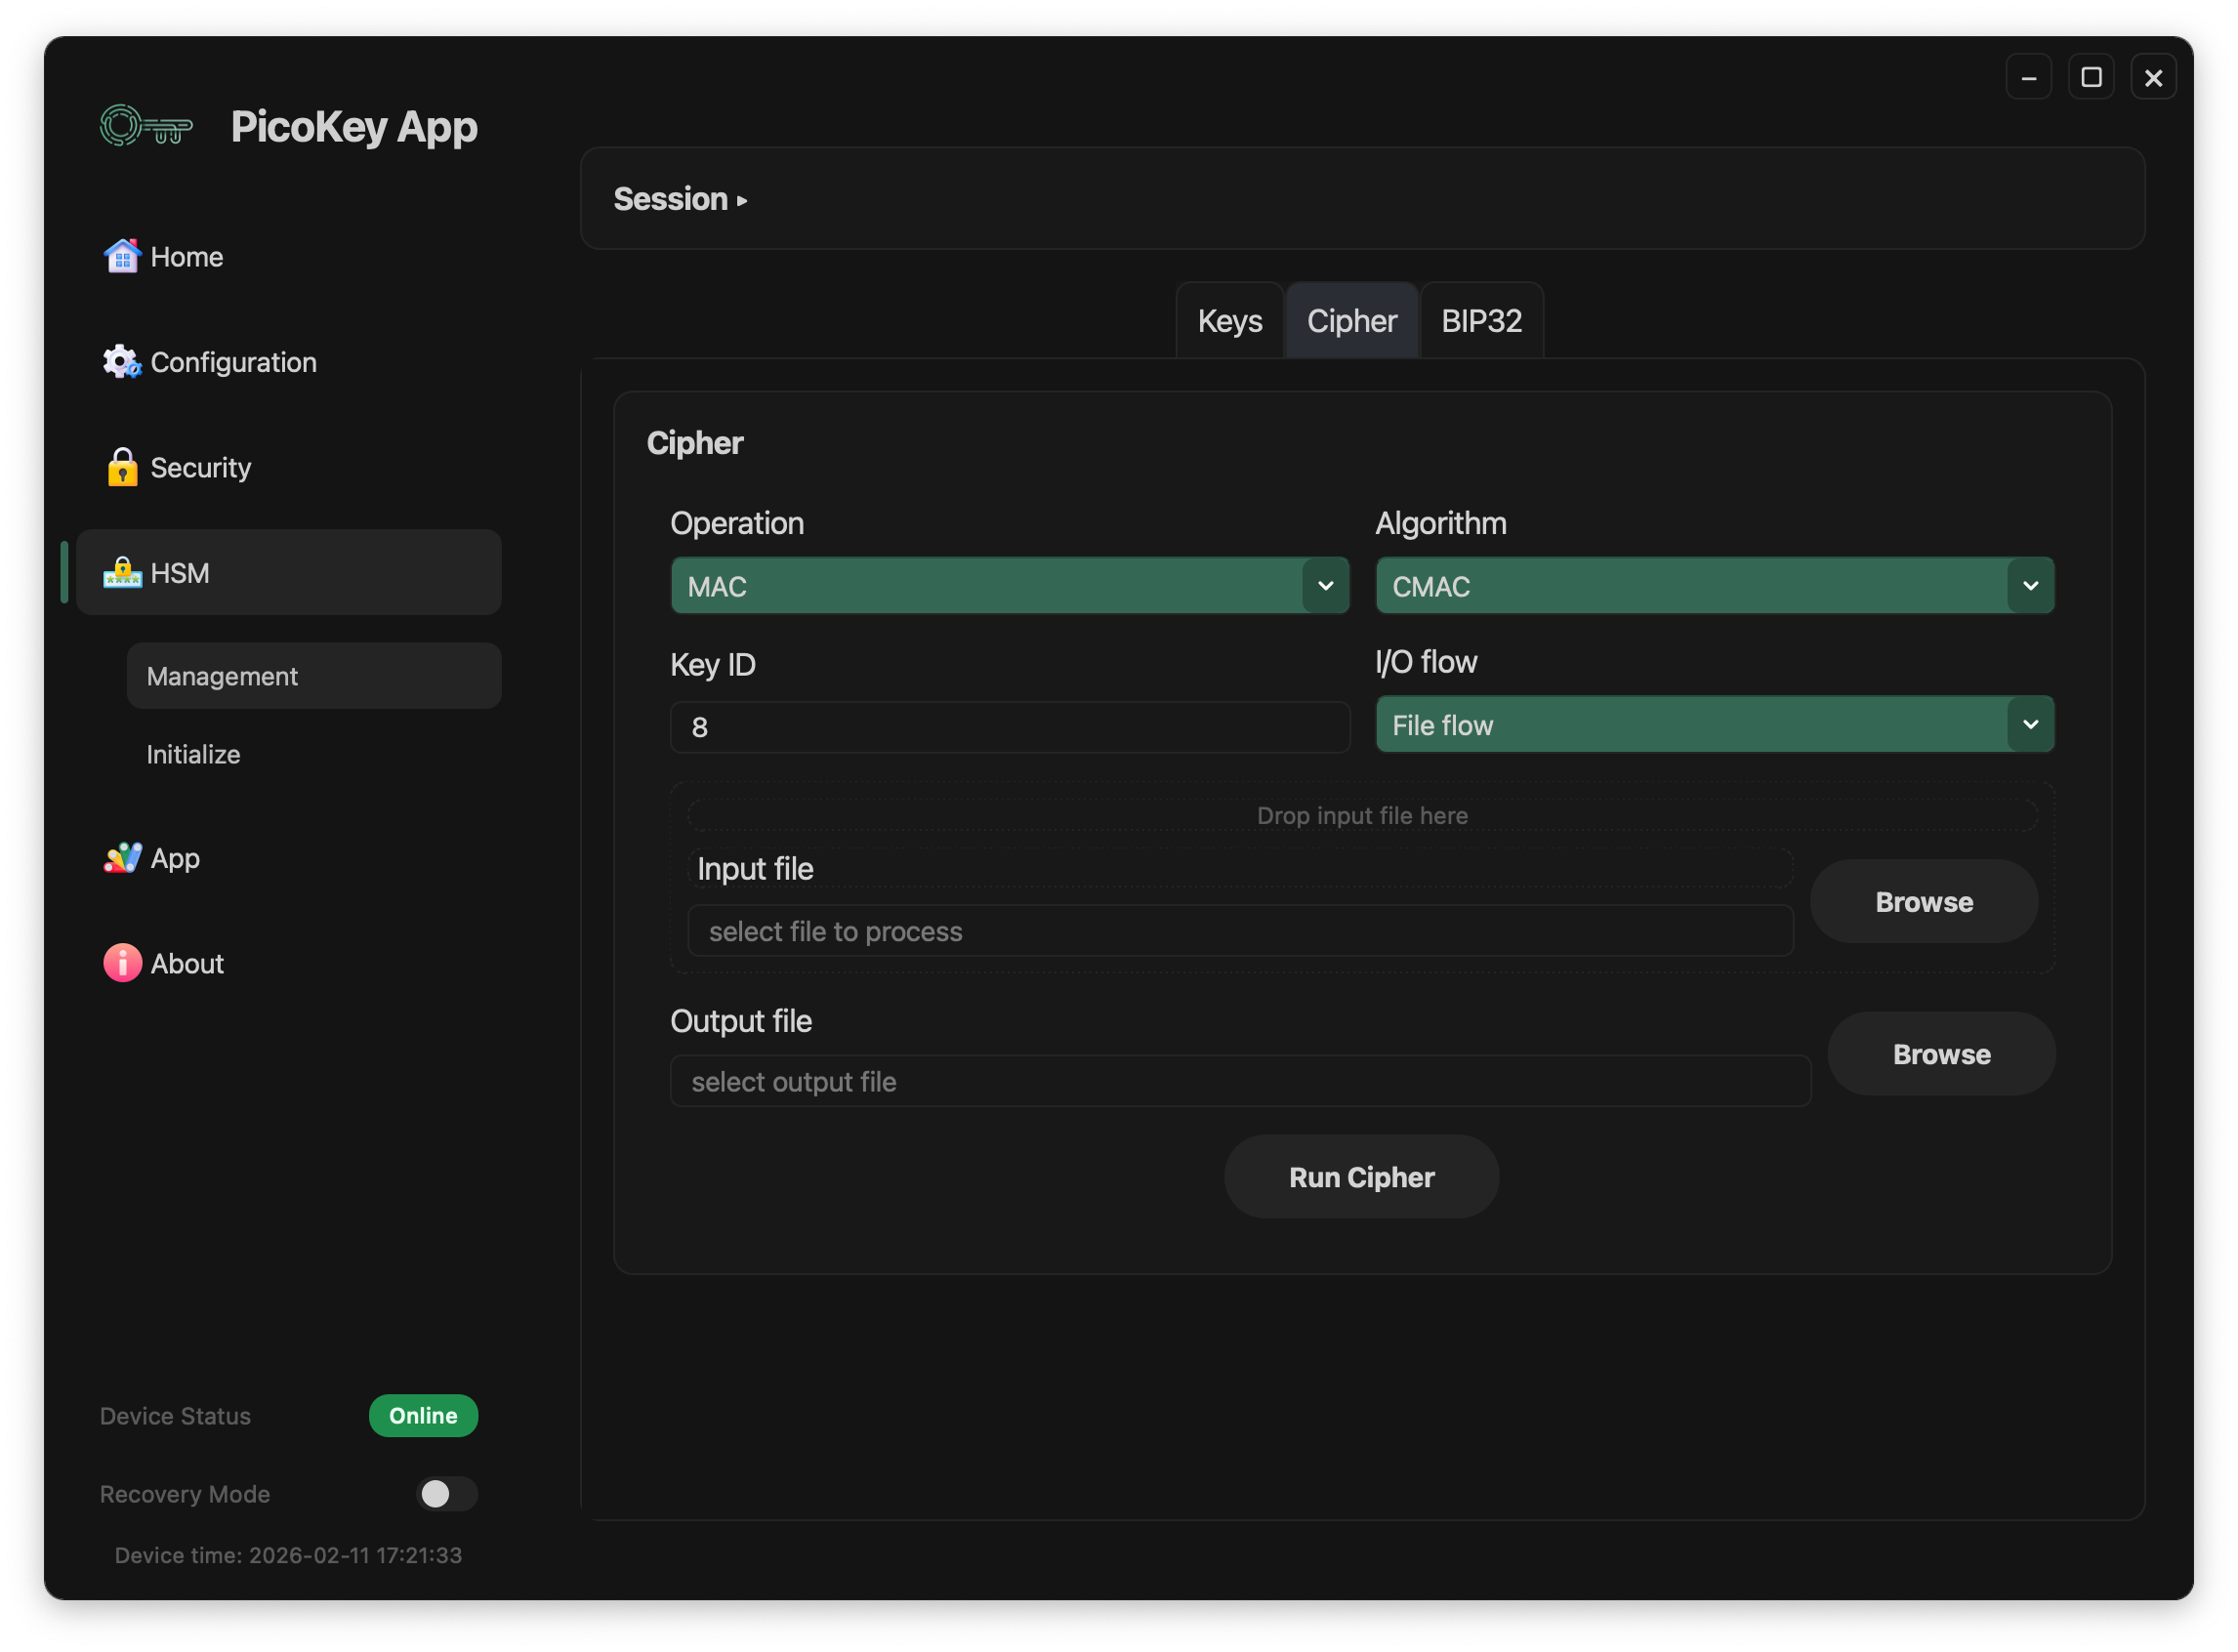
File flow
Use files as input and output.
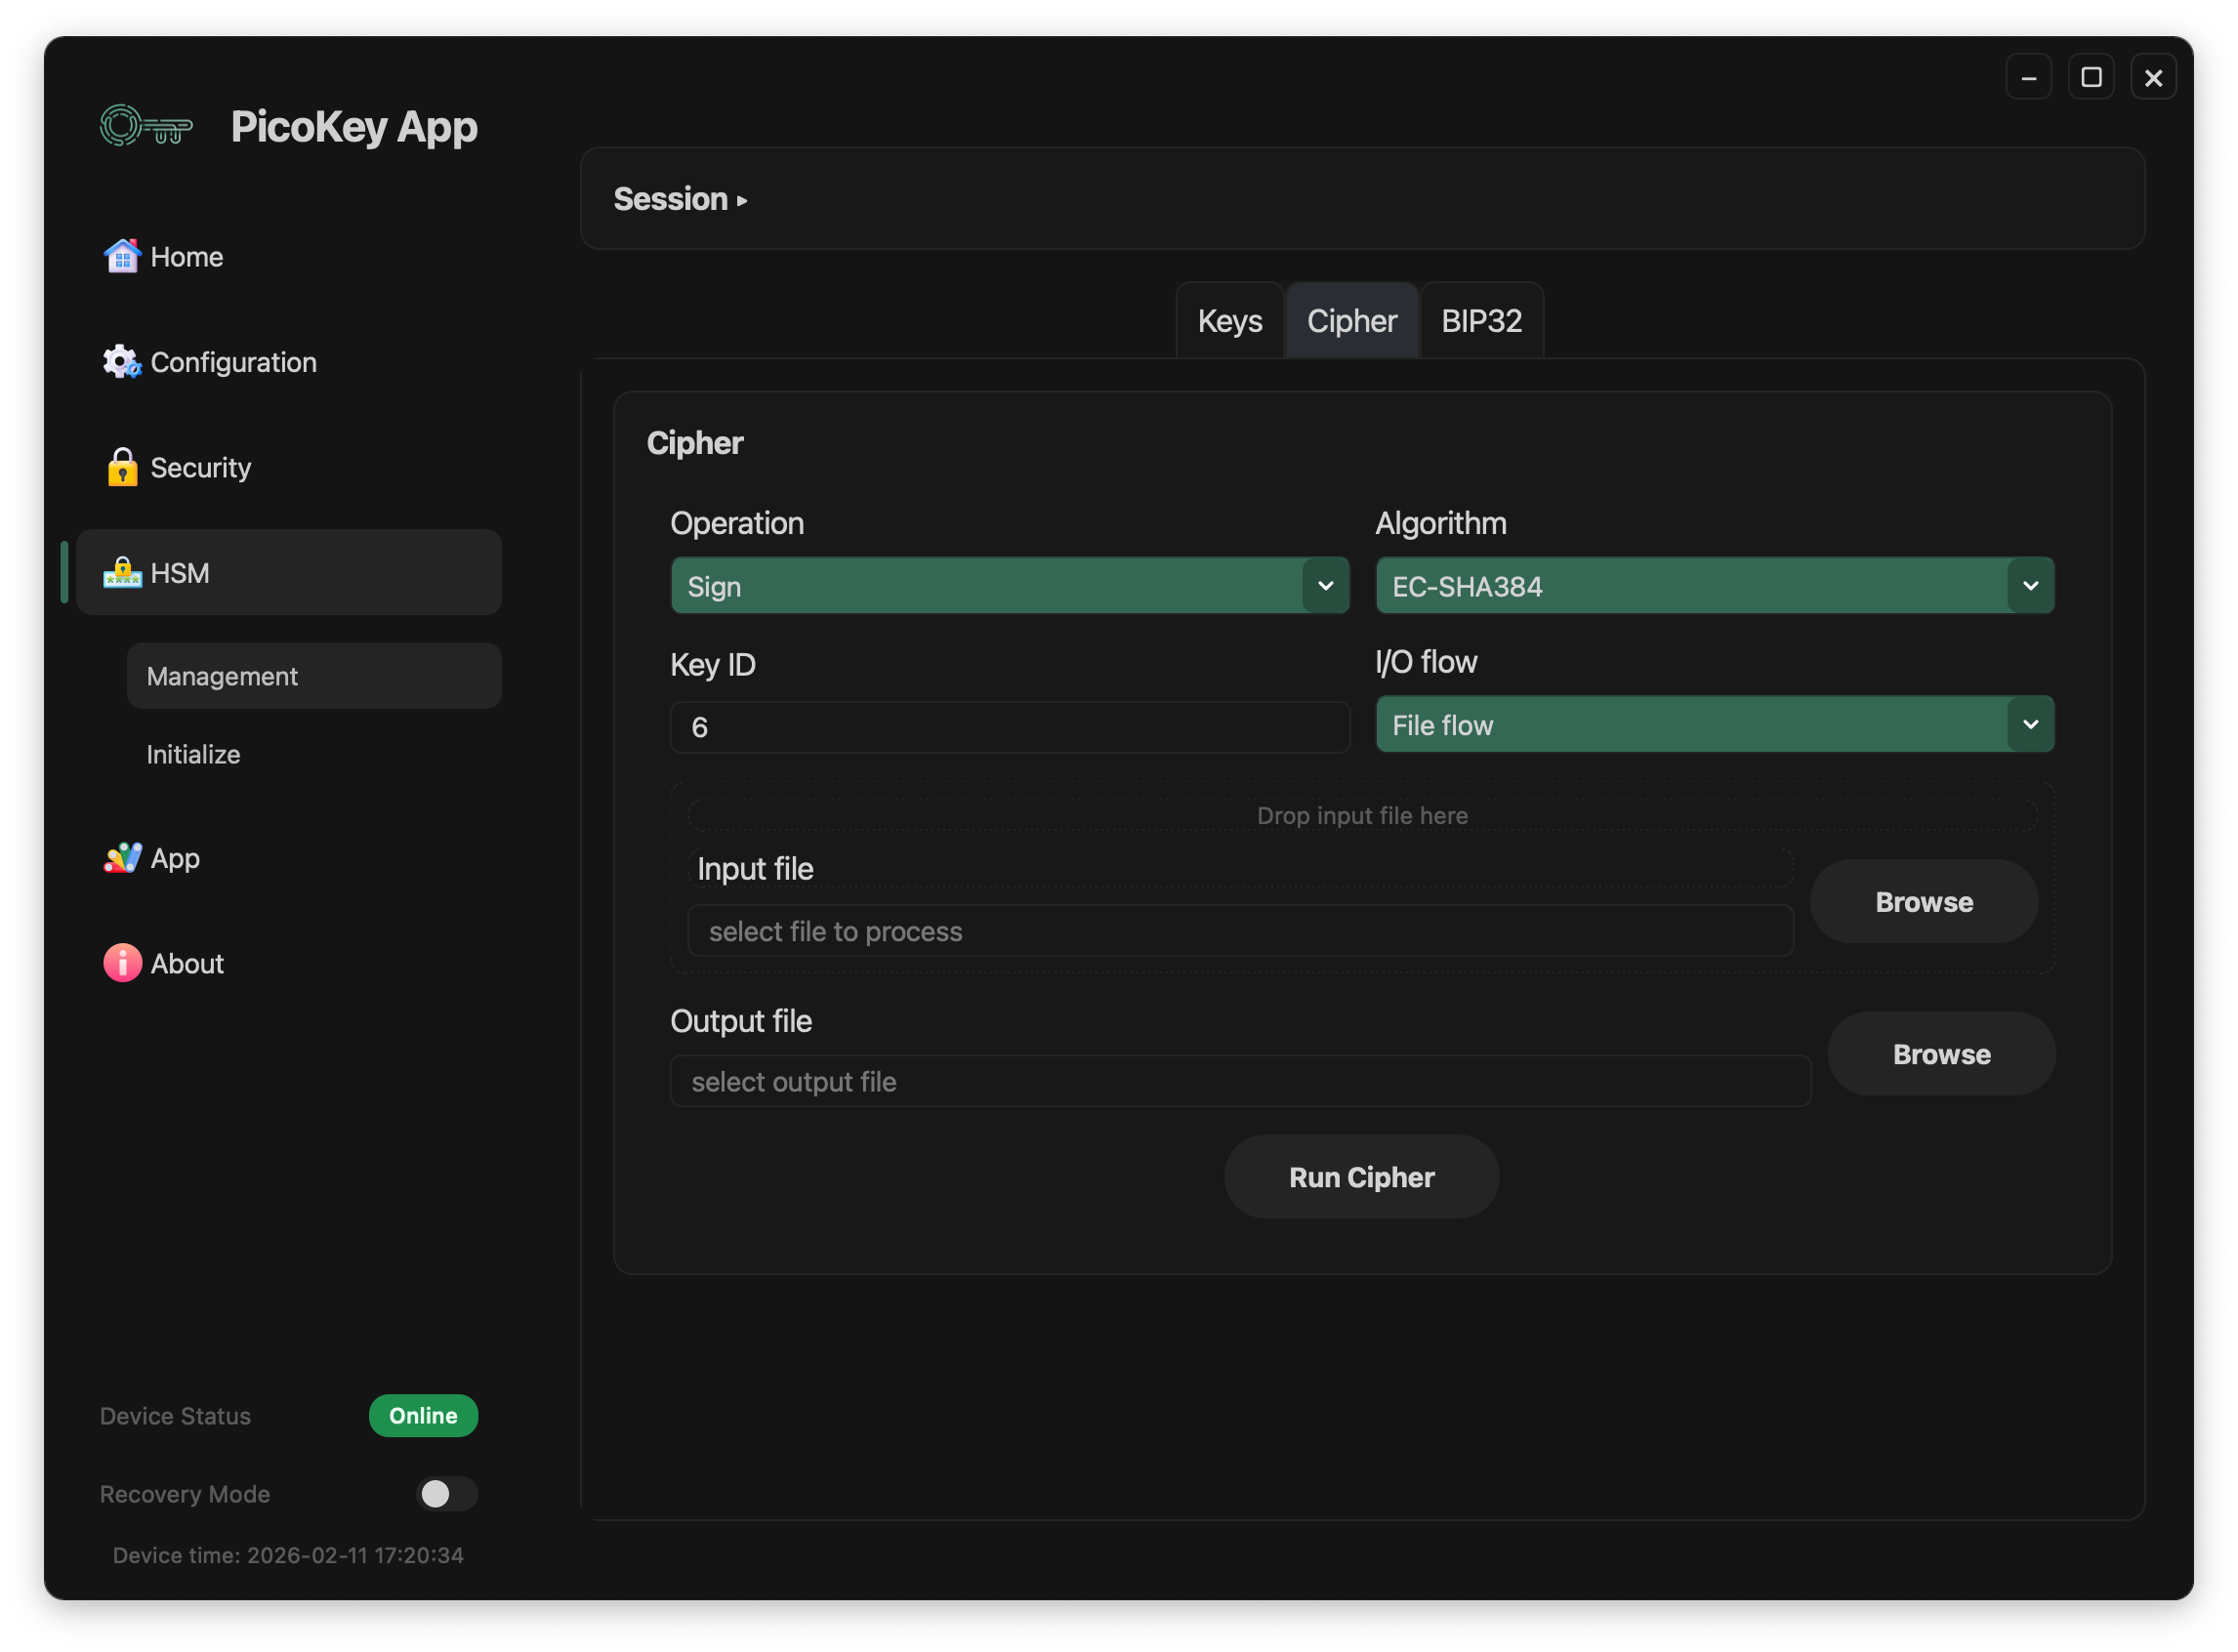
The file flow reads from Input file or the drop zone, then writes the result to Output file. Use the Browse buttons to choose the paths.
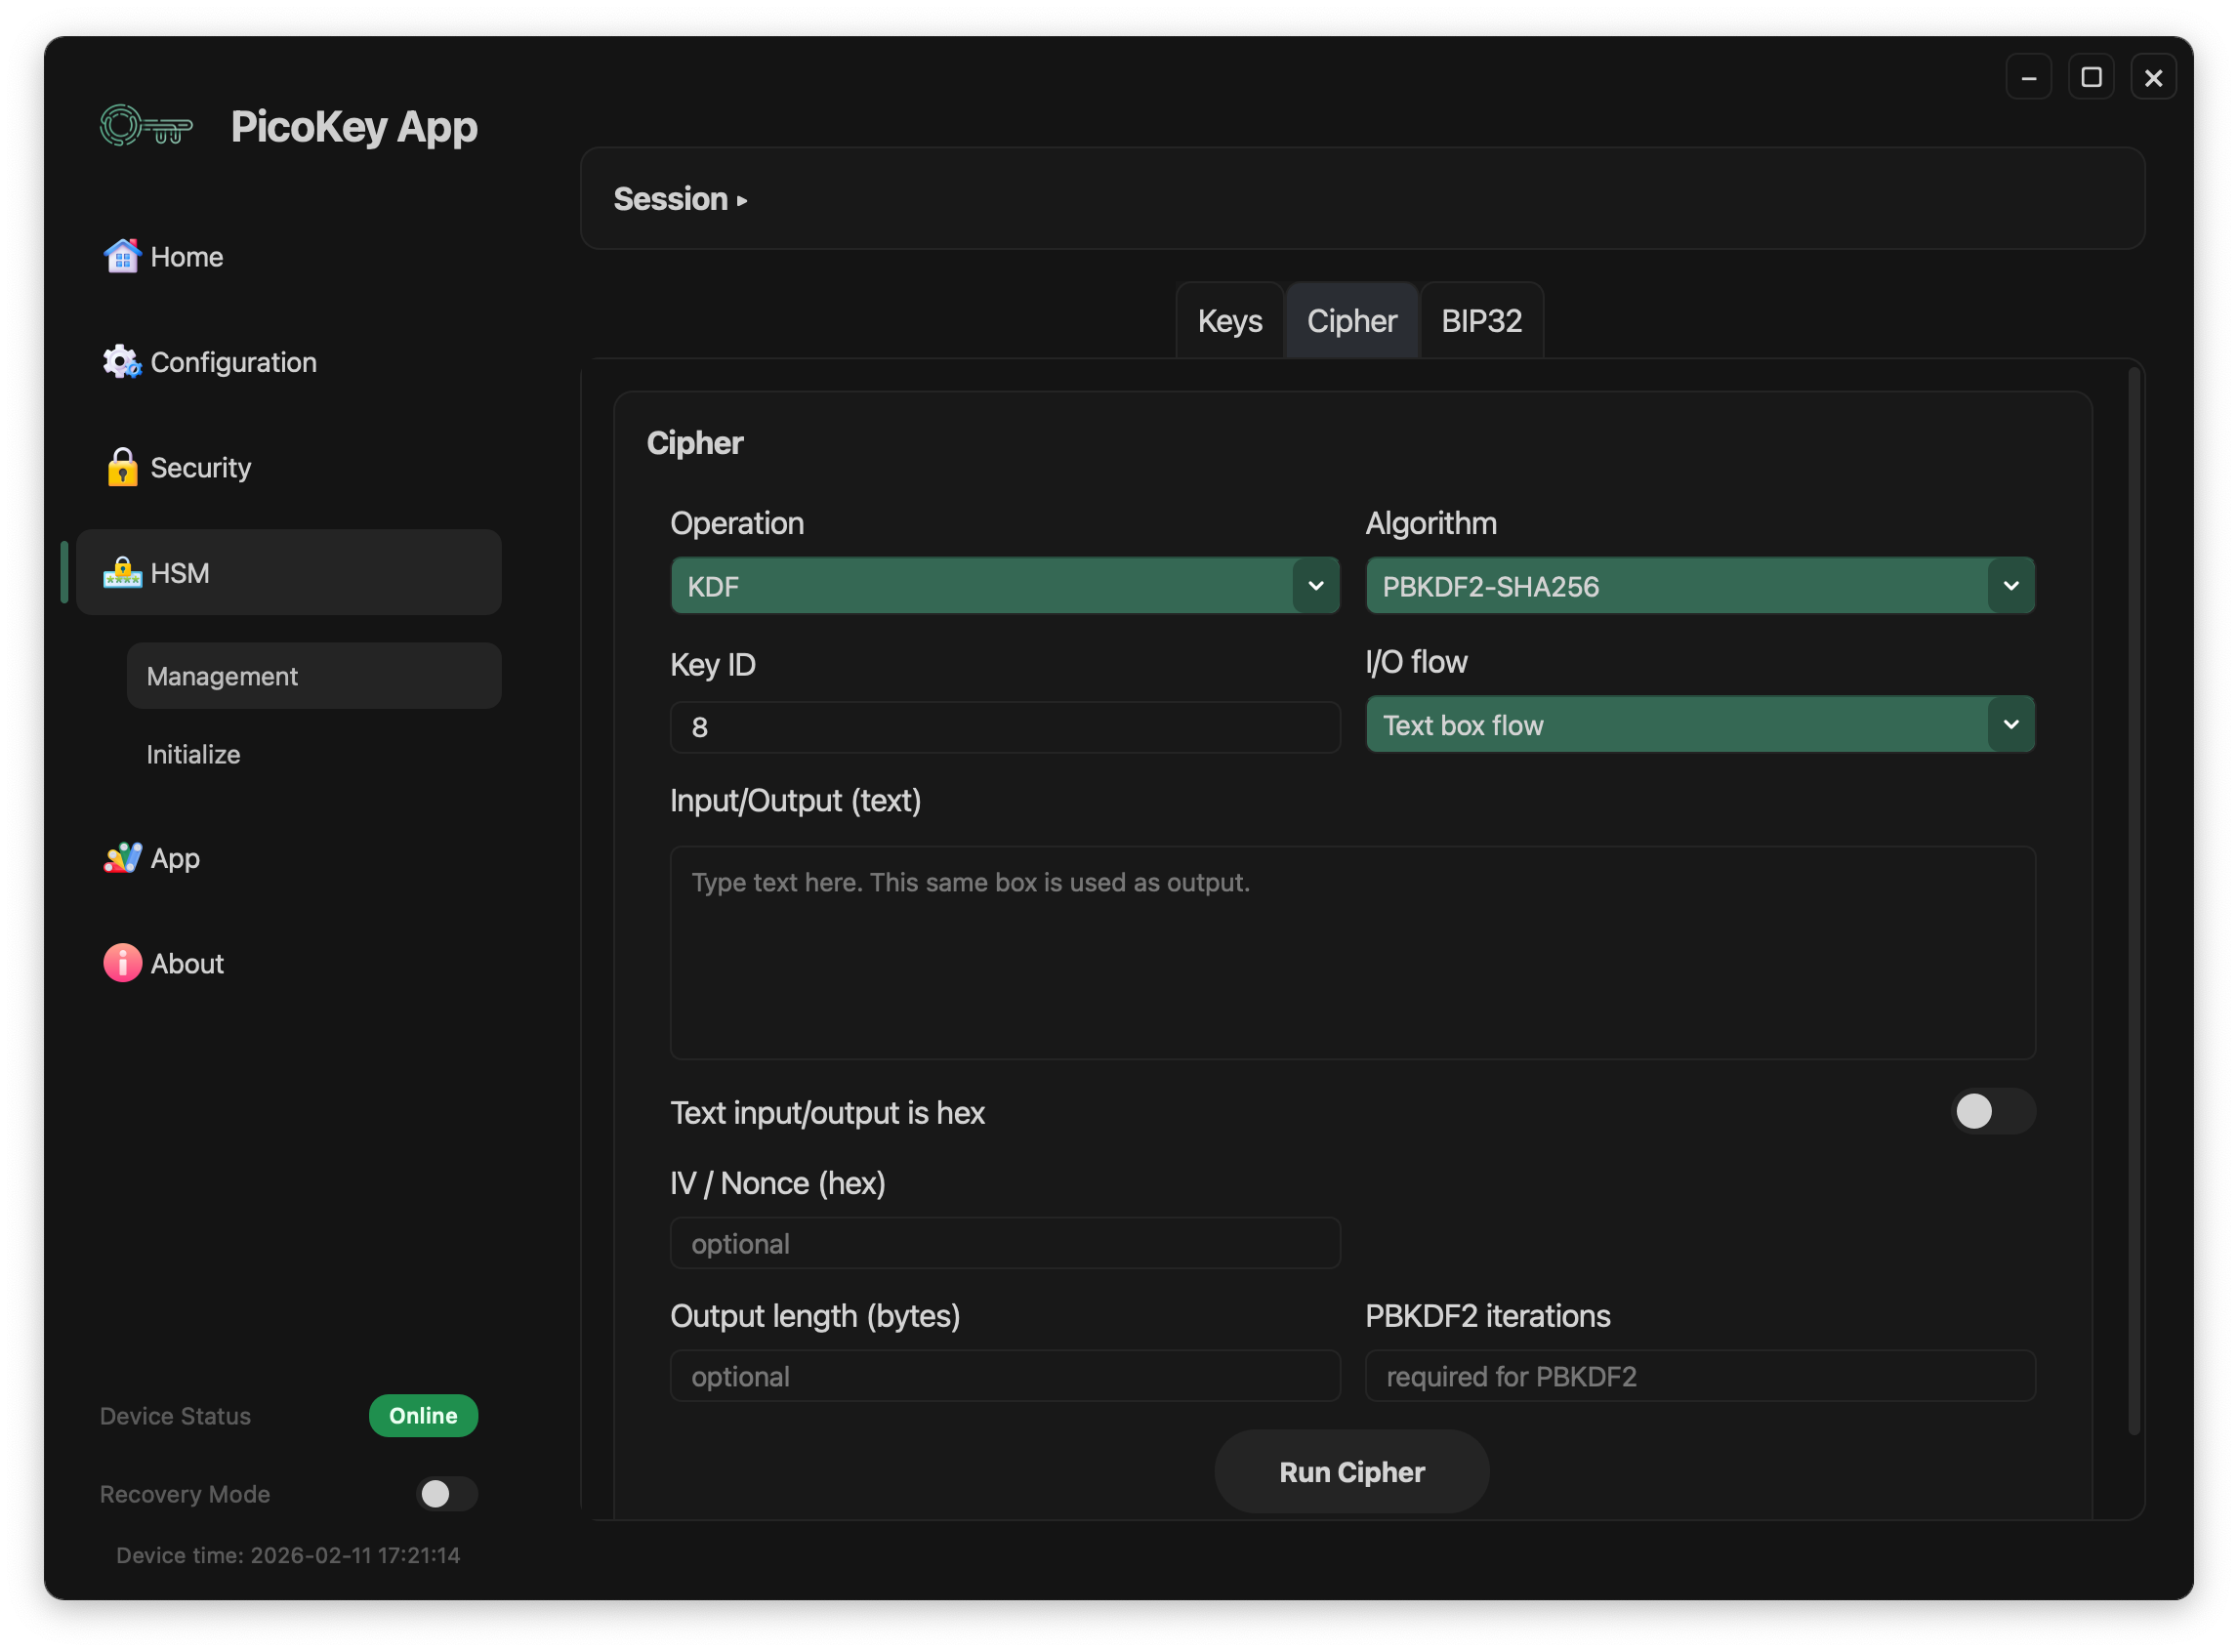
Text box flow
Use a single text area for both input and output.
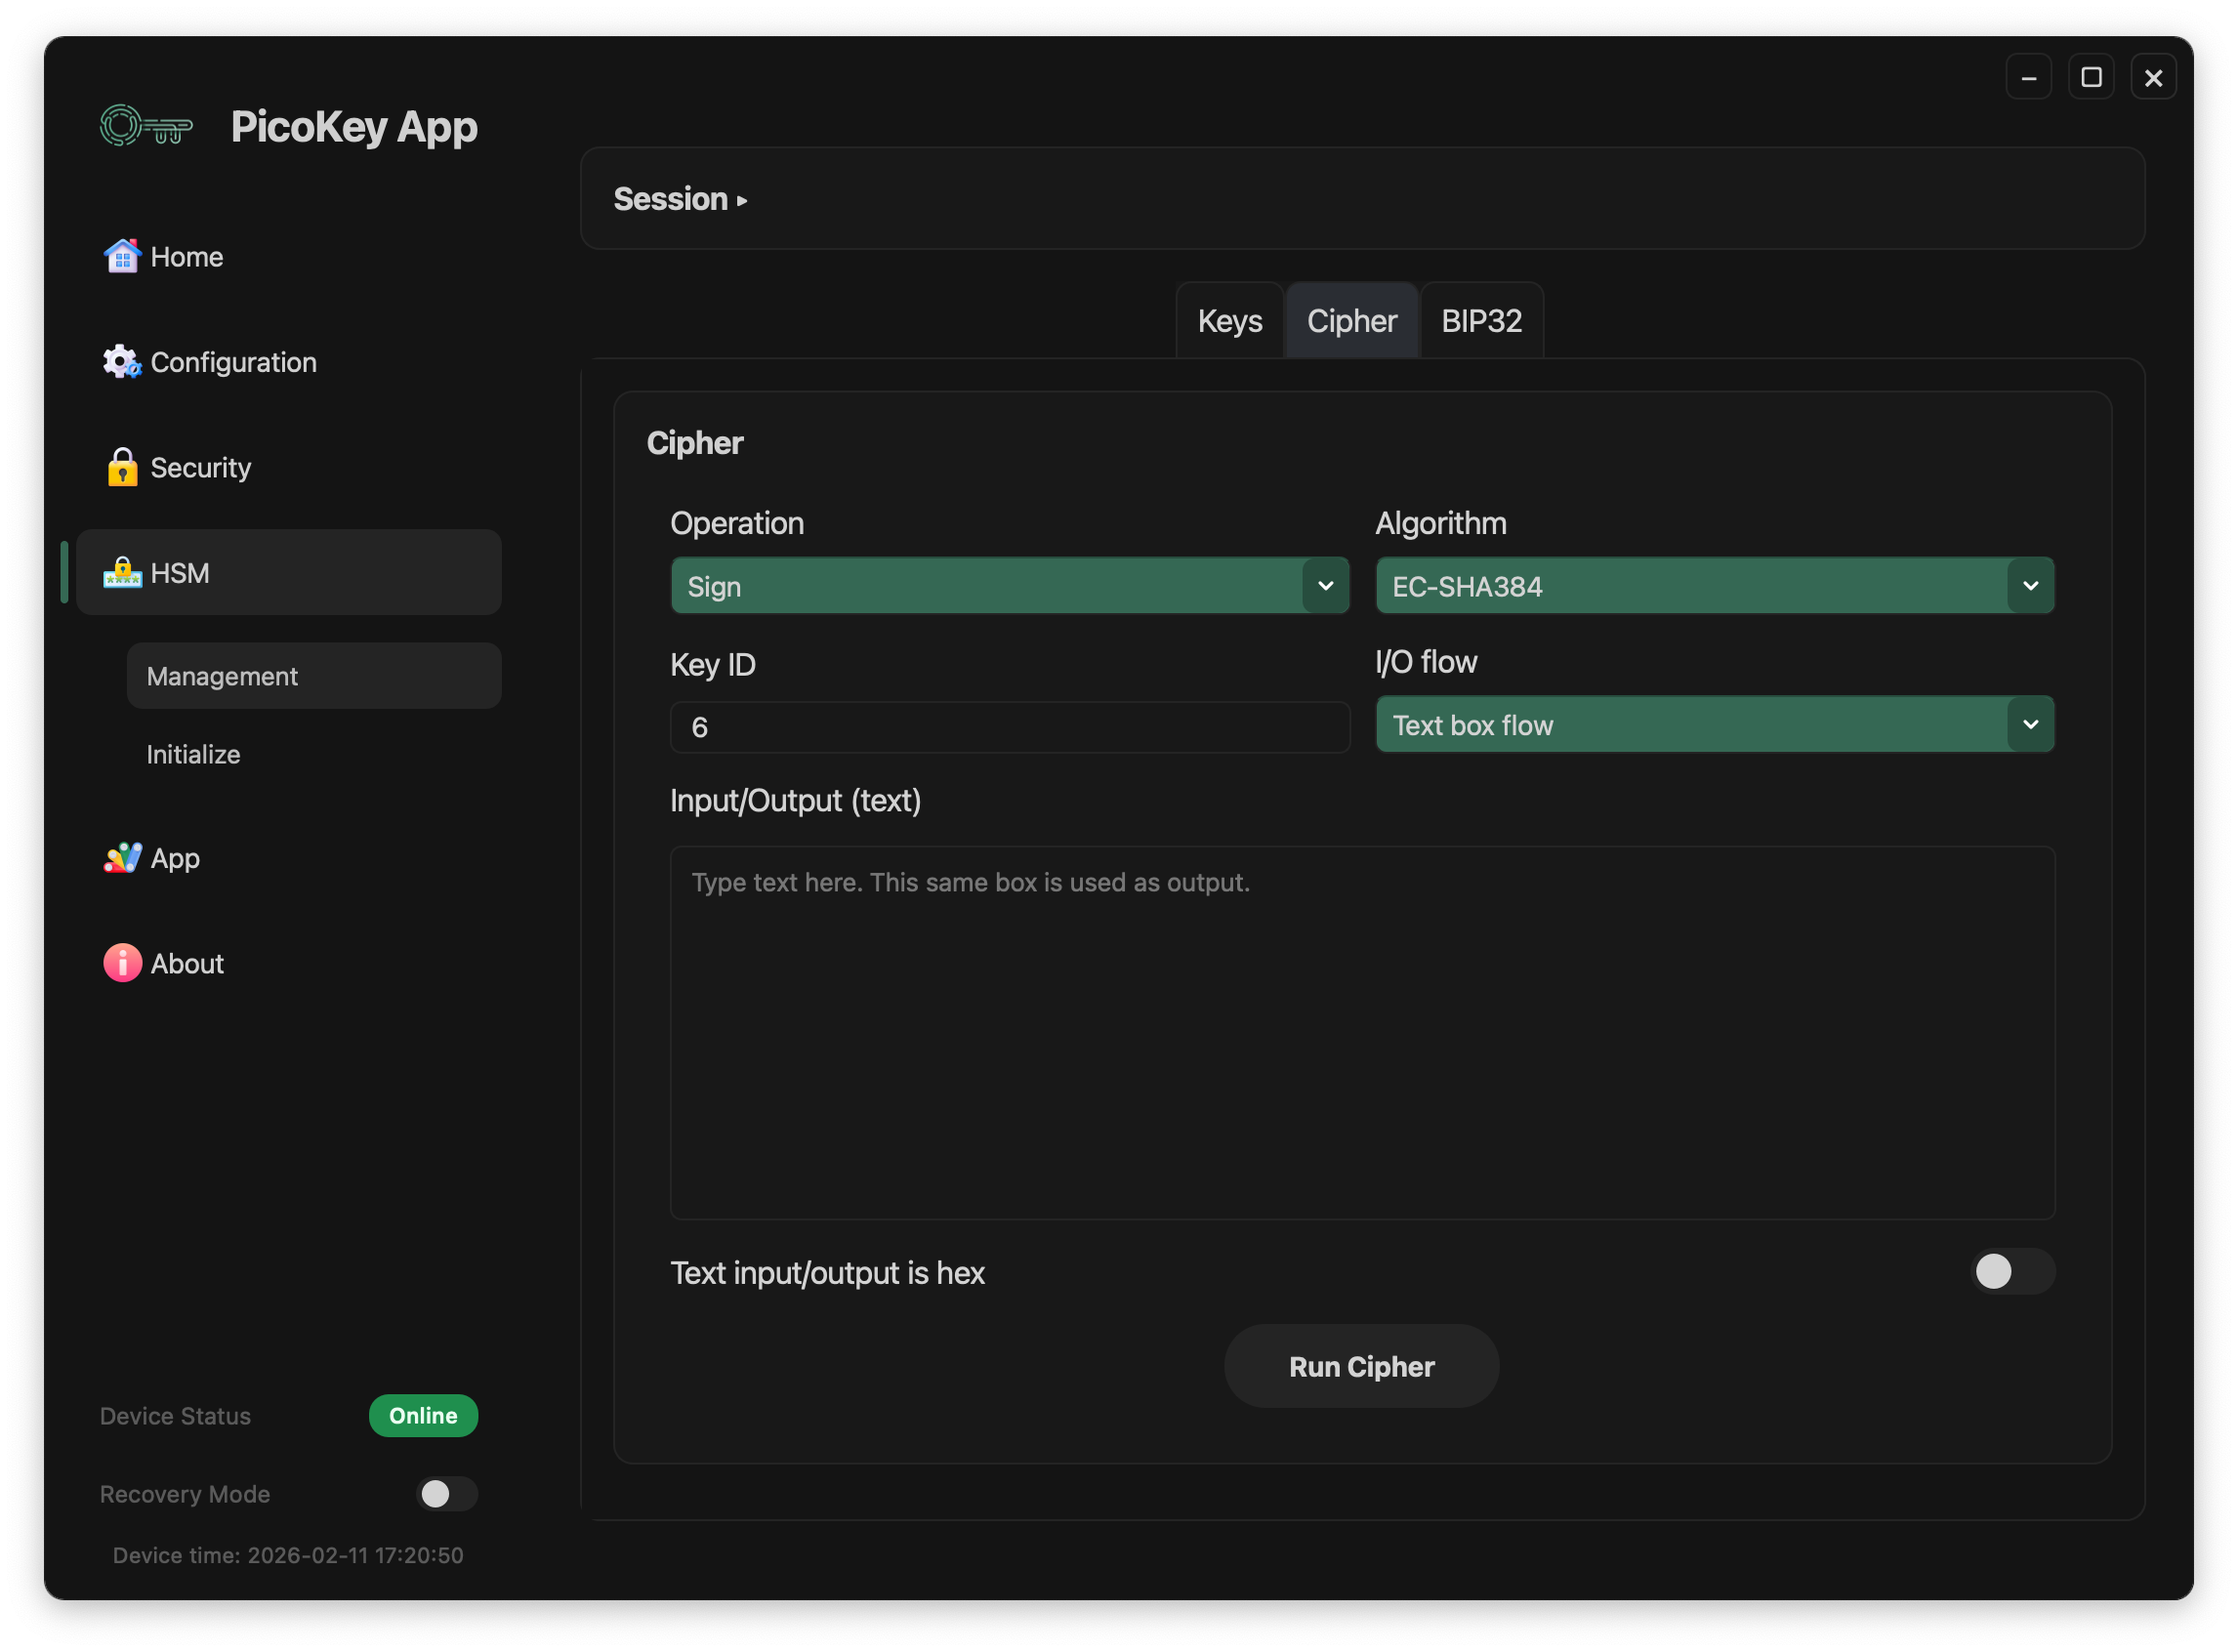
Enter plaintext, data, or signing input in the text box. After the operation,
the app replaces the input with the result. Use Text input/output is hex to
switch between plain text and hexadecimal input/output.
Operation-specific fields
Encrypt/Decryptwith AEAD/stream-like modes can require IV / Nonce (hex) and optional AAD (text or hex).MACuses file/text input and writes tag output.KDFcan include Output length (bytes) and, for PBKDF2, PBKDF2 iterations.
Algorithm availability by key type
EdDSA keys (ed25519, ed448)
- Only
Signis available. - The only signature algorithm is
EDDSA.
Other ECC keys
Signsupports:EC-RAWEC-SHA1EC-SHA224EC-SHA256EC-SHA384EC-SHA512
RSA keys
Signsupports:RSA-RAWRSA-PKCS1RSA-PKCS1-SHA1RSA-PKCS1-SHA224RSA-PKCS1-SHA256RSA-PKCS1-SHA384RSA-PKCS1-SHA512RSA-PSSRSA-PSS-SHA1RSA-PSS-SHA224RSA-PSS-SHA256RSA-PSS-SHA384-
RSA-PSS-SHA512 -
Decryptsupports: RSA-RAWRSA-PKCS1RSA-OAEP
AES keys (symmetric keys)
Encrypt/Decryptsupport:CHACHAPOLYAES-ECBAES-CBC(input length must be a multiple of 16 bytes)AES-OFBAES-CFBAES-GCMAES-CCMAES-CTR-
AES-XTS -
MACsupports: CMACHMAC-SHA1HMAC-SHA224HMAC-SHA256HMAC-SHA384-
HMAC-SHA512 -
KDFsupports: HKDF-SHA256HKDF-SHA384HKDF-SHA512PBKDF2-SHA1PBKDF2-SHA224PBKDF2-SHA256PBKDF2-SHA384PBKDF2-SHA512X963-SHA1X963-SHA224X963-SHA256X963-SHA384X963-SHA512
Note
The selector omits algorithms for operations that the selected key type does not support.